Published: 2006-03-15,
:2006-03 - 15を発表しました、
Last Updated: 2006-03-15 22:35:06 UTC by Johannes Ullrich (Version: 1)
最新アップデート:2006-03-15 ヨハンネス・ウルリッヒによっての22:35:06の UTC (バージョン:1)
Major news media reported today about a large child port sting operation, which resulted in 27 arrests in several countries. In this context, if you find / observe such activity, please report it in the US to the National Center for Missing and Exploited Children.
Please DO NOT send us any samples or links, but report it to the National Center's Cyber Tipline (see link on their home page).
今日いくつかの国で27の逮捕をもたらした大きい子供ポートおとり捜査について報告された主要なニュース・メディア。 この文脈で、もしあなたがこのような活動を見いだして / 観察するなら、どうか行方不明の、そして利用された子供たちのためにそれを合衆国で国立センターに報告してください。 どうか我々にサンプルあるいはリンクを送ってくれないでください、しかしそれを国立センターのサイバー・ Tipline に報告してください((彼・それ)らのホームページでリンクを見てください)。
The National Center for Missing and Exploited Children is tasked by the US government to coordinate the response in such cases and will forward reports to the appropriate law enforcement entities. Let us know if you know about similar entities in other countries and I will add respective links.
行方不明の、そして利用された子供たちのための国立センターは米国の政府によってこのような場合応答を調整する仕事を与えられて、そして適切な法の執行エンティティーへの報告を転送するでしょう。 我々にあなたが他の国々で類似のエンティティーについて知っている、そして私がそれぞれのリンクを加えるであろうかどうか知らせてください。
Published: 2006-03-15,
:2006-03 - 15を発表しました、
Last Updated: 2006-03-15 21:44:20 UTC by Johannes Ullrich (Version: 2(click to highlight changes)
)
最新アップデート:2006-03-15 ヨハンネス・ウルリッヒによっての21:44:20の UTC (バージョン:2(変更を強調するクリック))
As covered in the pre-announcement, Microsoft released two bulletins today:
同じぐらい発表前でカバーされていて、マイクロソフトは今日2つのブレティンをリリースしました:
This update fixes a number of different Excel vulnerabilities, and a "Malformed Routing Slip" vulnerability which affects muliple Office components.
この更新は多くの異なったエクセル弱点と muliple オフィスコンポーネントに影響を与える「身体障害のルーティングスリップ」弱点を直します。
All the vulnerabilities come down to the same issue: If you open a malformed file, an attacker could get control of the system as the user opening the file.
すべての弱点が同じ問題に帰着します:もしあなたが身体障害のファイルを開くなら、攻撃者がシステムのコントロールをファイルを開いているユーザーとして手に入れることができるでしょう。
If you use Microsoft Office, you should apply this patch quickly.
もしあなたがマイクロソフトオフィスを使うなら、あなたは速くこのパッチを用いるべきです。
UPDATE: 2006-03-15: PoC exploits have been released. The patch window is closing rapidly.
更新してください:2006-03-15: PoC exploit がリリースされました。 パッチウインドウは急速に閉じています。
It may be possible for a regular user to obtain the privileges assigned to a service. A lower privileged user could change the configuration for a service in order to have it execute code or modify the system in other ways, once the service is running at the higher privilege (e.g. 'system').
通常のユーザーがサービスに割り当てられた特典を得ることは可能であるかもしれません。 より低い恵まれているユーザーがそれがコードを実行するようにするか、あるいは、かつて、サービスがより高い特典で走っている他の方法でのシステム(例えば「システム」)を修正するために形状をサービスと交換することができました。
This vulnerability has been disclosed for a while now. It is important to note that a "service" is not just a "server". Services typically have to run at a higher privilege level as they require access to files across multiple users, and access to system resources.
この弱点は今しばらくの間明らかにされました。 「サービス」が「サーバー」ではないことを指摘することは重要です。 (彼・それ)らが多数のユーザー全体に渡るファイルへのアクセスとシステムリソースへのアクセスを必要とする(とき・から・につれて・ように)、サービスが典型的により高い特典レベルの割合で続けなければなりません。
SubVirt is a new proof-of-concept rootkit created by Microsoft Research and the University of Michigan. The idea is to install a rootkit that inserts itself at a lower level than the OS and then give the user a virtual machine environment that if successful, looks just like their own. An inexperienced user then might never realize that they aren’t really in control, and all of their software defenses might not realize it either.
SubVirt はマイクロソフト研究とミシガン大学によって作られる新しい「コンセプトの証明」 rootkit です。 考えは OS より低いレベルにおいてそれ自身を挿入する rootkit をインストールして、そして次にユーザーにもし成功しているなら、(彼・それ)ら自身のものとまったく同じように見えるバーチャルマシン環境を与えることです。 未経験のユーザーがそれから決して(彼・それ)らが本当に主導権を掌握していないことを悟らないかもしれません、そして(彼・それ)らのすべてのソフトウェアディフェンスは同様それを理解しないかもしれません。
Why is Microsoft building a better rootkit? We aren’t too sure, but to paraphrase this eWeek article
published on the 10th, Microsoft hopes to use the perspective of the attacker to better understand the needs of the defender. It sounds to us a bit like the scientists that were researching nuclear fission without really thinking about the final use for the bomb that they were helping to build.
マイクロソフトはなぜもっと良い rootkit を構築していますか? 我々はあまり確かではありません、しかし10番に出版されたこの eWeek 論文を言い替えるために、マイクロソフトは攻撃者の見地をもっと良く擁護者の必要を理解するために使うことを望みます。 それは本当に(彼・それ)らが作るのを手伝っていた爆弾の最終の用途について考えないで核分裂を研究していた科学者とちょっと同じように我々に鳴ります。
In any case the concept isn’t entirely new. In 1993, PMBS was discovered, a stealth virus as they were termed at the time. PMBS was a boot virus that traveled via infected floppy disks. Once it infected a machine, it copied itself into extended memory, switched the computer into protected mode and ran virtual V86 machine. DOS and other applications where then run from that virtual PC.
いずれにしてもコンセプトは完全に新しくありません。 1993年に、(彼・それ)らがその時呼ばれたように、 PMBS は見いだされた、内密ウイルスでした。 PMBS は感染しているフロッピーディスクによって移動したブートウイルスでした。 それがマシンを感染させた途端に、それはそれ自身を拡張メモリにコピーして、プロテクトモードの中にコンピュータを切り替えて、そしてバーチャル V86 マシンを動かしました。 DOS と他のアプリケーションはそれから場合はそのバーチャルPCから走ります。
Published: 2006-03-14,
:2006-03 - 14を発表しました、
Last Updated: 2006-03-14 19:09:39 UTC by Johannes Ullrich (Version: 1)
最新アップデート:2006-03-14 ヨハンネス・ウルリッヒによっての19:09:39の UTC (バージョン:1)
As covered in the pre-announcement, Microsoft released two bulletins today:
同じぐらい発表前でカバーされていて、マイクロソフトは今日2つのブレティンをリリースしました:
This update fixes a number of different Excel vulnerabilities, and a "Malformed Routing Slip" vulnerability which affects muliple Office components.
この更新は多くの異なったエクセル弱点と muliple オフィスコンポーネントに影響を与える「身体障害のルーティングスリップ」弱点を直します。
All the vulnerabilities come down to the same issue: If you open a malformed file, an attacker could get control of the system as the user opening the file.
すべての弱点が同じ問題に帰着します:もしあなたが身体障害のファイルを開くなら、攻撃者がシステムのコントロールをファイルを開いているユーザーとして手に入れることができるでしょう。
If you use Microsoft Office, you should apply this patch quickly.
もしあなたがマイクロソフトオフィスを使うなら、あなたは速くこのパッチを用いるべきです。
It may be possible for a regular user to obtain the privileges assigned to a service. A lower privileged user could change the configuration for a service in order to have it execute code or modify the system in other ways, once the service is running at the higher privilege (e.g. 'system').
通常のユーザーがサービスに割り当てられた特典を得ることは可能であるかもしれません。 より低い恵まれているユーザーがそれがコードを実行するようにするか、あるいは、かつて、サービスがより高い特典で走っている他の方法でのシステム(例えば「システム」)を修正するために形状をサービスと交換することができました。
This vulnerability has been disclosed for a while now. It is important to note that a "service" is not just a "server". Services typically have to run at a higher privilege level as they require access to files across multiple users, and access to system resources.
この弱点は今しばらくの間明らかにされました。 「サービス」が「サーバー」ではないことを指摘することは重要です。 (彼・それ)らが多数のユーザー全体に渡るファイルへのアクセスとシステムリソースへのアクセスを必要とする(とき・から・につれて・ように)、サービスが典型的により高い特典レベルの割合で続けなければなりません。
Published: 2006-03-14,
:2006-03 - 14を発表しました、
Last Updated: 2006-03-14 15:47:18 UTC by Jim Clausing (Version: 1)
最新アップデート:2006-03-14 ジム・クロージングによっての15:47:18の UTC (バージョン:1)
In one of the updates to Pat's story
on Sunday, I mentioned that we had heard McAfee would make its tool to restore files that had been incorrectly quarantined by the bad DAT publically available at some point. Well, one of our readers, Mark, has pointed out to us, that the tool is now available (thanx, Mark). Follow the link in the 13 Mar update at http://vil.nai.com/vil/content/v_138884.htm
.
更新の1つでパットの物語に日曜日に、私は我々が(すでに) McAfee がある時点に間違って良くない DAT によって隔離されたファイルを復元するそのツールを publically に提供するであろうということを耳にしていたと述べました。 まあ、我々の読者の1人、マーク、が、我々に、ツールが今利用可能です(thanx 、マーク)ことを指摘しました。 http://vil.nai.com/vil/content/v_138884.htm において3月13日の更新でリンクをたどってください。
Published: 2006-03-12,
:2006-03 - 12を発表しました、
Last Updated: 2006-03-12 15:05:01 UTC by Swa Frantzen (Version: 1)
最新アップデート:2006-03-12 Swa Frantzen によっての15:05:01の UTC (バージョン:1)
Arms Race ?
軍備競争?
As with anything the bad guys do, they react to anything we do to try to prevent them from having success. One of the things we told our users was to ignore alerting messages that their bank (and any other bank they are not a customer of) seems to send them and tells them their account has been abused. It seems that it is finally having it's effect as the phishers are changing tactics.
悪人がする何と同じようにでも、(彼・それ)らは我々が(彼・それ)らが成功を遂げるのを阻止しようとするためにする何にでも反応します。 我々が我々のユーザーに(彼・それ)らの銀行(そして(彼・それ)らが顧客ではない他のいかなる銀行でも)が(彼・それ)らを送るように思われて、そして(彼・それ)らに(彼・それ)らの記述を話すというメッセージに警告することを無視するはずであったと言ったものの1つが乱用されました。 phishers が戦術を変えている(とき・から・につれて・ように)、それが最終的にそれを持っていることの効果であるように思われます。
These kind of arms races require us to increase awareness constantly and to make users more resilient all the time. If we fail this our users, customers, ... will fall prey and we will have failed our users and/or customers in the end.
これらの種類の軍備競争が我々にいつも認識を増やして、そしていつもユーザーをいっそう回復力があるようにするように要求します。 もし我々がこれに失敗するなら、我々のユーザー、顧客、は・・・えじきになるでしょう、そして我々は結局我々のユーザーそして/あるいは顧客に落第点を付けてしまっているでしょう。
Example of one of these new phishing attempts
これらの新しいフィッシングの試みの1つの例
From: Chase Manhattan Bank

差出人:チェース・マンハッタン銀行

To: victim@example.com

宛先: victim@example.com

Subject: [ $20 Reward Survey ]

件名:[20ドルの報酬調査]


Dear Chase Bank Customer,

親愛なるチェース銀行顧客、
CONGRATULATIONS!
おめでとうございます!
You have been chosen by the Chase Manhattan Bank online department
あなたはチェース・マンハッタン銀行のオンラインの課によって選ばれました to take part in our quick and easy 5 question survey.
我々の速い、そして容易な5つの質問調査に参加するために。 In return we will credit $20 to your account - Just for your time!
お返しに我々は20ドルをあなたのアカウントに返金するでしょう - ただあなたの時間! Helping us better understand how our customers feel benefits everyone.
我々がもっと良く我々の顧客がどのように感じるか理解するのを手伝うことは皆に役立ちます。 With the information collected we can decide to direct a number of
我々が数を方向づけることに決めることができる集められたインフォメーションで changes to improve and expand our online service.
我々のオンライン・サービスを改善して、そして拡張するために変わります。 We kindly ask you to spare two minutes of your time
我々は親切にあなたにあなたの時間の2分を与えるように求めます in taking part with this unique offer!
このユニークな申し出で参加することにおいて!
Confirm Now your $20 Reward Survey with Chase Online? Reward
チェースと一緒にオンラインで今あなたの20ドルの報酬調査を確認します? 報酬 services.
サービス。
The information you provide us is all non-sensitive and anonymous
あなたが我々を提供するというインフォメーションはまったく機密性が高くなくて、そして匿名です No part of it is handed down to any third party groups.
それの部分がサードパーティーグループに伝えられません。 It will be stored in our secure database for maximum of 3 days
それは3日の最大限の間我々の安全なデータベースにストアされるでしょう while we process the results of this nationwide survey.
我々がこの全国的な調査の結果を処理する間に。
Please do not reply to this message. For any inquiries, contact
どうかこのメッセージに答えないでください。 どんな調査のためにでも、連絡を取ってください Customer Service.
顧客サービス。
It was formatted much more fancy in html, but I chose not to show that here.
それは html でずっとおしゃれでフォーマットされました、しかし私はここでそれを見せないことに決めました。
Of course the link in there doesn't go to anything owned by JPMorgan Chase & Co.
もちろんあそこのリンクはJ.P.モーガン・チェース社によって所有される何かに行きません。
Now let's have a look at that website collecting so called "non-sensitive and anonymous" information.
今いわゆる「機密性が高くない、そして匿名の」インフォメーションを集めているそのウェブサイトをひと目見ましょう。
It starts out all rather innocent
それはまったくどちらかと言うと罪がないように始まります
but then it goes on to ask you more details. Details that are far from non-sensitive and anonymous. But remember the psychology: the user just has answered a whopping 5 questions and is now going to get his 20 bucks. He'll even sell his mother for it, or at least tell them her name along with what is going to cost him much more than that 20 bucks he'll never get.
けれどもそれからそれはあなたにもっと多くの詳細を尋ねることを続いてします。 機密性が高くなくて、そして匿名であることからほど遠い詳細。 けれども心理学を覚えていてください:ユーザーはちょうど巨大な5つの質問に答えたところであって、そして今彼の20ドルを得ようとしています。 彼は彼の母親をそれのために売りさえするか、あるいはそれよりずっと多く彼に彼が決して得ないであろう20ドルの費用がかかろうとしているものとともに少なくとも(彼・それ)らに彼女の名前を話すでしょう。
The details they want to know:
(彼・それ)らが知ることを望む細部:
New tactic: better servers
新しい戦術:もっと良いサーバー
Unfortunately they are also getting better on the technology side:
不幸にも(彼・それ)らは技術側で同じくもっと良くなっています:
"premium" service from a well known name on the Internet
インターネット上のよく知られている名前からの「保険料」サービス
very redundant DNS service
非常に不必要な DNS サービス
lots of servers
たくさんのサーバー
chaseonline.new-reward-survey.us. 600 IN CNAME  premium.geo.yahoo.akadns.net.

chaseonline.new - 報酬 - survey.us 。 600の IN CNAME  premium.geo.yahoo.akadns.net 。

premium.geo.yahoo.akadns.net. 300 IN    A       66.218.79.174

premium.geo.yahoo.akadns.net 。 300 IN      A        66.218.79.174

premium.geo.yahoo.akadns.net. 300 IN    A       66.218.79.175

premium.geo.yahoo.akadns.net 。 300 IN      A        66.218.79.175

premium.geo.yahoo.akadns.net. 300 IN    A       66.218.79.177

premium.geo.yahoo.akadns.net 。 300 IN      A        66.218.79.177

premium.geo.yahoo.akadns.net. 300 IN    A       66.218.79.184

premium.geo.yahoo.akadns.net 。 300 IN      A        66.218.79.184

premium.geo.yahoo.akadns.net. 300 IN    A       66.218.79.185

premium.geo.yahoo.akadns.net 。 300 IN      A        66.218.79.185

premium.geo.yahoo.akadns.net. 300 IN    A       66.218.79.186

premium.geo.yahoo.akadns.net 。 300 IN      A        66.218.79.186

premium.geo.yahoo.akadns.net. 300 IN    A       66.218.79.188

premium.geo.yahoo.akadns.net 。 300 IN      A        66.218.79.188

premium.geo.yahoo.akadns.net. 300 IN    A       66.218.79.173

premium.geo.yahoo.akadns.net 。 300 IN      A        66.218.79.173
The not so good news goes on:
それほど良くないニュースが続けます:
Worst of all the responses you receive when reporting these things to the abuse contacts of some service providers is so far below par that getting this shut down in a hurry isn't likely. I hope the banks have a bit more pull than this handler.
あなたがこれらのことを若干のサービスプロバイダの虐待の接触に報告することは非常にパーの下に遠いので、これを得ることはすぐにシャットダウンしたとき受けるすべての回答の最悪はありそうではありません。 私は銀行がこの調教師よりもう少し多くの引きを持っていることを希望します。
Yes I know that exposing this more publicly will increase the odds that other rivaling groups will start to use these techniques as well, but after having received half a dozen of these myself my guess is that they already know.
はい私はいっそう公的にこれを見せることは他に匹敵しているグループが同様にこれらのテクニックを使い始めるであろうという見込みを増やすであろうことを知っています、しかし、私自身これらの半ダースを受け取った後で、私の推測は(彼・それ)らがすでに知っているということです。
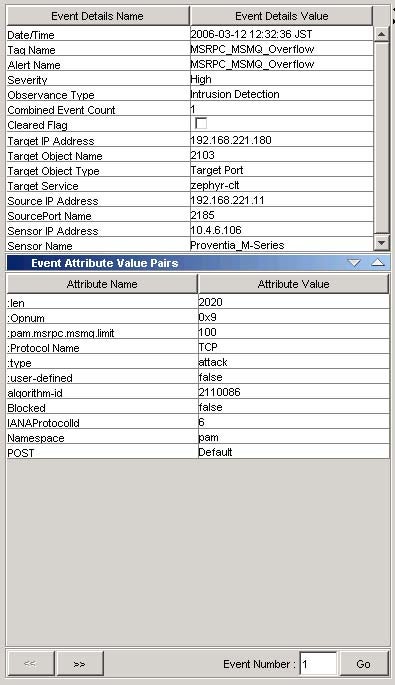
Microsoft Windows 2000 SP3 および SP4、Windows XP SP1、および Windows 98 は、メッセージキュー (MSMQ) コンポーネントの未チェックのバッファによって引き起こされるバッファオーバーフローに対して脆弱です。 MSMQ コンポーネントがインストールされている場合、リモートの攻撃者は特殊な形式の TCP メッセージを送信することで、バッファをオーバーフローさせ、システム上で任意のコードを実行する可能性があります。攻撃者がこの脆弱点を悪用してシステムの完全な制御権を得ると、システム上のアカウントを表示、変更、削除、または新規作成することも可能です。
この脆弱点の解決方法
Microsoft Security Bulletin を参照して、システムに適切なパッチを適用します。