■コメント

RPC によるメモリの割り当てのサービス拒否を対象とした。

実証コマンドの実行結果とIDSでの検知状況について

http://www.microsoft.com/japan/technet/security/advisory/911052.mspx

■攻撃元

192.168.221.110 RedHat


■攻撃対象

192.168.221.180 Win2K+SP4


■実証コマンド


!------------------------------------------!
Memory leak when sending upnp_getdevicelist request
Coded by: Winny Thomas :-)
NevisLabs
Nevis Networks, Pune, INDIA
!------------------------------------------!

[*] Resolving 192.168.221.180: OK
[*] Sending SMB Negotiate request: OK
[*] Sending Null Session request: OK
[*] Sending Null Session request: OK
[*] Sending Tree Connect request: OK
[*] Sending NT Creat AndX request: OK
[*] Sending DCE RPC Bind UPNPMGR request: OK
[*] UPNPMGR upnp_getdevicelist request: nca_s_fault_ndr

[root@linux ]#


■対象への影響

コードを実行する事により対象ホストのメモリー使用率が上昇する事を確認する。


■Provenita

Low SMB_Filename 16
Low Windows_Null_Session 8
Low MSRPC_PlugAndPlay_Detected 6


Event Number : 15
Date/Time : 2006-01-07 17:31:13 JST
Tag Name : SMB_Filename
Alert Name : SMB_Filename
Severity : Low
Tag Brief Description :
Observance Type : Intrusion Detection
Combined Event Count : 1
Cleared Flag : No
Target DNS Name :
Target IP Address : 192.168.37.180
Target Object Name : 445
Target Object Type : Target Port
Target Service :
Source DNS Name :
Source IP Address : 192.168.221.110
SourcePort Name : 1025
Sensor DNS Name :
Sensor IP Address : 192.168.221.11
Sensor Name : network_sensor_1

Attribute Value Pairs for Event Number : 15
Attribute Name : :filename
Attribute Value : \\192.168.221.180\IPC$
Attribute Name : :intruder-ip-addr
Attribute Value : 192.168.221.110
Attribute Name : :intruder-port
Attribute Value : 1025
Attribute Name : :victim-ip-addr
Attribute Value : 192.168.37.180
Attribute Name : :victim-port
Attribute Value : 445
Attribute Name : algorithm-id
Attribute Value : 3000501
Attribute Name : IANAProtocolId
Attribute Value : 6
Attribute Name : Packet DestinationAddress
Attribute Value : 192.168.37.180
Attribute Name : Packet DestinationPort
Attribute Value : 445
Attribute Name : Packet DestinationPortName
Attribute Value : microsoft-ds
Attribute Name : Packet SourceAddress
Attribute Value : 192.168.221.110
Attribute Name : Packet SourcePort
Attribute Value : 1025


Event Number : 16
Date/Time : 2006-01-07 17:31:13 JST
Tag Name : SMB_Filename
Alert Name : SMB_Filename
Severity : Low
Tag Brief Description :
Observance Type : Intrusion Detection
Combined Event Count : 1
Cleared Flag : No
Target DNS Name :
Target IP Address : 192.168.37.180
Target Object Name : 445
Target Object Type : Target Port
Target Service :
Source DNS Name :
Source IP Address : 192.168.221.110
SourcePort Name : 1025
Sensor DNS Name :
Sensor IP Address : 192.168.221.11
Sensor Name : network_sensor_1

Attribute Value Pairs for Event Number : 16
Attribute Name : :filename
Attribute Value : \browser
Attribute Name : :intruder-ip-addr
Attribute Value : 192.168.221.110
Attribute Name : :intruder-port
Attribute Value : 1025
Attribute Name : :victim-ip-addr
Attribute Value : 192.168.37.180
Attribute Name : :victim-port
Attribute Value : 445
Attribute Name : algorithm-id
Attribute Value : 3000501
Attribute Name : IANAProtocolId
Attribute Value : 6
Attribute Name : Packet DestinationAddress
Attribute Value : 192.168.37.180
Attribute Name : Packet DestinationPort
Attribute Value : 445
Attribute Name : Packet DestinationPortName
Attribute Value : microsoft-ds
Attribute Name : Packet SourceAddress
Attribute Value : 192.168.221.110
Attribute Name : Packet SourcePort
Attribute Value : 1025


Event Number : 17
Date/Time : 2006-01-07 17:38:07 JST
Tag Name : Windows_Null_Session
Alert Name : Windows_Null_Session
Severity : Low
Tag Brief Description :
Observance Type : Intrusion Detection
Combined Event Count : 1
Cleared Flag : No
Target DNS Name :
Target IP Address : 192.168.221.180
Target Object Name : 445
Target Object Type : Target Port
Target Service :
Source DNS Name :
Source IP Address : 192.168.221.110
SourcePort Name : 1028
Sensor DNS Name : iss-sp2
Sensor IP Address : 10.4.6.100
Sensor Name : network_sensor_1

Attribute Value Pairs for Event Number : 17
Attribute Name : :CLIENT
Attribute Value : HOD
Attribute Name : :intruder-ip-addr
Attribute Value : 192.168.221.110
Attribute Name : :intruder-port
Attribute Value : 1028
Attribute Name : :SERVER
Attribute Value : TEST-LR0IS30UAX
Attribute Name : :victim-ip-addr
Attribute Value : 192.168.221.180
Attribute Name : :victim-port
Attribute Value : 445
Attribute Name : algorithm-id
Attribute Value : 3102039
Attribute Name : IANAProtocolId
Attribute Value : 6
Attribute Name : LOGEVIDENCE
Attribute Value : Default
Attribute Name : Packet DestinationAddress
Attribute Value : 192.168.221.180
Attribute Name : Packet DestinationPort
Attribute Value : 445
Attribute Name : Packet DestinationPortName
Attribute Value : microsoft-ds
Attribute Name : Packet SourceAddress
Attribute Value : 192.168.221.110
Attribute Name : Packet SourcePort
Attribute Value : 1028


Event Number : 25
Date/Time : 2006-01-07 17:38:11 JST
Tag Name : MSRPC_PlugAndPlay_Detected
Alert Name : MSRPC_PlugAndPlay_Detected
Severity : Low
Tag Brief Description :
Observance Type : Intrusion Detection
Combined Event Count : 1
Cleared Flag : No
Target DNS Name :
Target IP Address : 192.168.221.180
Target Object Name : 445
Target Object Type : Target Port
Target Service :
Source DNS Name :
Source IP Address : 192.168.221.110
SourcePort Name : 1028
Sensor DNS Name : iss-sp2
Sensor IP Address : 10.4.6.100
Sensor Name : network_sensor_1

Attribute Value Pairs for Event Number : 25
Attribute Name : :intruder-ip-addr
Attribute Value : 192.168.221.110
Attribute Name : :intruder-port
Attribute Value : 1028
Attribute Name : :UUID
Attribute Value : 8d9f4e40-a03d-11ce-8f69-08003e30051b
Attribute Name : :victim-ip-addr
Attribute Value : 192.168.221.180
Attribute Name : :victim-port
Attribute Value : 445
Attribute Name : algorithm-id
Attribute Value : 3118016
Attribute Name : IANAProtocolId
Attribute Value : 6
Attribute Name : LOGEVIDENCE
Attribute Value : Default
Attribute Name : Packet DestinationAddress
Attribute Value : 192.168.221.180
Attribute Name : Packet DestinationPort
Attribute Value : 445
Attribute Name : Packet DestinationPortName
Attribute Value : microsoft-ds
Attribute Name : Packet SourceAddress
Attribute Value : 192.168.221.110
Attribute Name : Packet SourcePort
Attribute Value : 1028


■Snort

01/07-17:30:52.429489 [**] [1:2466:6] NETBIOS SMB-DS IPC$ unicode share access [**] [Classification: Generic Protocol Command Decode] [Priority: 3] {TCP} 192.168.221.110:1025 -> 192.168.37.180:445
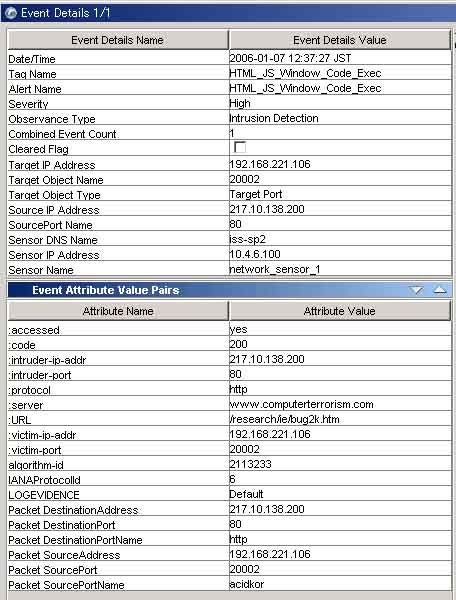

■シグネチャの説明

http://xforce.iss.net/xforce/xfdb/20783


■Proventiaでの検知(IDS)


MS05-054


■参考情報

Secunia Security Advisory: SA15546
Microsoft Internet Explorer "window()" Denial of Service Weakness
http://secunia.com/advisories/15546/

Microsoft Internet Explorer Web page
Internet Explorer Home
http://www.microsoft.com/windows/ie/default.mspx

FrSIRT Security Advisory FrSIRT/ADV-2005-2509
Microsoft Internet Explorer "window()" Code Execution Vulnerability
http://www.frsirt.com/english/advisories/2005/2509

Microsoft Security Advisory (911302)
Vulnerability in the way Internet Explorer Handles onLoad Events Could Allow Remote Code Execution
http://www.microsoft.com/technet/security/advisory/911302.mspx

CERT Vulnerability Note VU#887861
Microsoft Internet Explorer vulnerable to code execution via scripting "window()" object
http://www.kb.cert.org/vuls/id/887861

Internet Security Systems Protection Alert, November 22, 2005
Internet Explorer Javascript Window() Remote Code Execution
http://xforce.iss.net/xforce/alerts/id/209

CVE
CVE-2005-1790
http://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2005-1790


----------------------------
■あまてらす
----------------------------

おはようございます。あまてらすです。


----------------------------
■不正なアクセス(日本を送信元とした攻撃)
----------------------------


自分の管理するグローバルIPアドレスが以下のリストに含まれている場合は、ウィルスまたはボットワームに感染している恐れが高いです。至急ウィルススキャンを実行される事を推奨します。


58.88.60.50 p1050-ipbf912marunouchi.tokyo.ocn.ne.jp
219.111.177.39 p6fb127.ymgcnt01.ap.so-net.ne.jp
218.47.126.97 i218-47-126-97.s02.a023.ap.plala.or.jp
218.45.67.153 218.45.67.153.eo.eaccess.ne.jp
218.45.54.72 fla03-072.wind.ne.jp
218.45.54.248 fla03-248.wind.ne.jp
218.45.54.198 fla03-198.wind.ne.jp
218.45.50.100 fla2407-100.wind.ne.jp
218.45.41.112 f041112.mctv.ne.jp
218.45.35.2 f035002.mctv.ne.jp
218.45.3.51 ppp31.aikis.or.jp
218.45.22.193 flets22-193.kamome.or.jp
218.45.173.212 k173212.ppp.asahi-net.or.jp
218.45.169.169 k169169.ppp.asahi-net.or.jp
218.45.168.69 k168069.ppp.asahi-net.or.jp
218.45.168.42 k168042.ppp.asahi-net.or.jp
218.45.168.225 k168225.ppp.asahi-net.or.jp
218.45.165.188 k165188.ppp.asahi-net.or.jp
218.45.139.41 u21845139041.hctv.ne.jp
218.45.138.160 u21845138160.hctv.ne.jp
218.45.111.143 flets-a-west-24-143.dsn.jp
218.45.111.104 flets-a-west-24-104.dsn.jp
218.45.110.6 flets-a-west-15-6.dsn.jp
218.45.110.204 flets-a-west-15-204.dsn.jp
218.45.107.59 flets-a-west-12-59.dsn.jp
218.44.52.12 f52.12.fgo.jp
218.44.107.86 i218-44-107-86.s02.a045.ap.plala.or.jp
218.43.92.31 p9031-adsao01tachib-acca.tokyo.ocn.ne.jp
218.43.49.152 p3152-ipbf412marunouchi.tokyo.ocn.ne.jp
218.43.2.121 p3121-ipad02niigatani.niigata.ocn.ne.jp
218.43.147.202 p2202-ipad02matuyama.ehime.ocn.ne.jp
218.43.132.238 p2238-ipad12sasajima.aichi.ocn.ne.jp
218.42.66.204 FLA1Acw204.tky.mesh.ad.jp
218.42.239.20 218-42-239-20.eonet.ne.jp
218.42.226.32 218-42-226-32.eonet.ne.jp
218.42.201.104 218-42-201-104.eonet.ne.jp
218.41.29.28 p291d1c.hyognt01.ap.so-net.ne.jp
218.41.15.131 p290f83.sitmnt01.ap.so-net.ne.jp
218.40.16.62 da2810-062.tiki.ne.jp
218.231.193.71 218.231.193.71.eo.eaccess.ne.jp
218.224.186.91 i218-224-186-91.s02.a022.ap.plala.or.jp
218.223.220.245 u245.d220223218.ctt.ne.jp
218.220.122.183 zaqdadc7ab7.zaq.ne.jp
218.219.247.105 l247105.ppp.asahi-net.or.jp
218.219.127.9 ppp2295.hakata07.bbiq.jp
218.218.130.124 OFSfa-03p3-124.ppp11.odn.ad.jp
218.110.85.157 p6e559d.sigant01.ap.so-net.ne.jp

202.225.237.39

FLA1Aab039.myg.mesh.ad.jp


■脆弱性の説明MSMS05-039

http://www.microsoft.com/japan/technet/security/Bulletin/MS05-039.mspx


■攻撃元

192.168.221.106 W2K

■攻撃対象

192.168.221.180 Win2K(English)


■実証コード

ターゲットIPと接続ポートを指定する。MS05-039の脆弱性が存在する場合、攻撃が成功する。

ms05039GUI.J


■影響

リモートからログインする事が可能である。

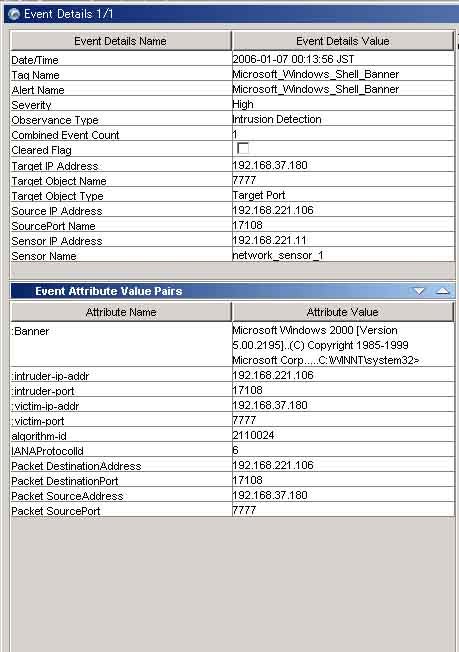
・オープンさせた7777ポートに対してtelnetで接続してみる。

Microsoft Windows 2000 [Version 5.00.2195]
(C) Copyright 1985-2000 Microsoft Corp.

C:\Documents and Settings\Administrator>telnet 192.168.37.180 7777


・コマンドプロンプトでアクセスする事ができた。

Microsoft Windows 2000 [Version 5.00.2195]
(C) Copyright 1985-1999 Microsoft Corp.

C:\WINNT\system32>


■Proventia

ツールを使用した攻撃の際、以下のイベントが検知しました。

High PlugAndPlay_BO 1
Low SMB_Filename 2
Low Windows_Null_Session 2
Low MSRPC_PlugAndPlay_Detected 1
Low Windows_Access_Error 1


オープンポートへ接続する際、以下のイベントが検知しました。

High Microsoft_Windows_Shell_Banner 1

※http://ameblo.jp/amaterasu/entry-10007760680.html


■Snort

01/07-00:46:35.520656 [**] [1:2466:6] NETBIOS SMB-DS IPC$ unicode share access [**] [Classification: Generic Protocol Command Decode] [Priority: 3] {TCP} 192.168.221.106:17337 -> 192.168.37.180:445

■コメント

脆弱性などを利用したオープンさせたポートに対して、リモートから接続する際検知します。

Port7777など不明なポートへの接続を検知した場合は、対象通信について確認する事をお勧めします。


■シグネチャの説明

http://xforce.iss.net/xforce/xfdb/12903


■Proventiaでの検知(IDS)

Microsoft_Windows_Shell_Banner


■パケット

N/A


■脆弱性の説明MSMS05-047

http://www.microsoft.com/japan/technet/security/Bulletin/MS05-047.mspx

http://xforce.iss.net/xforce/bulletins/microsoft/MS05-047

■攻撃元

192.168.221.11 W2K

■攻撃対象

192.168.221.180 Win2K(English)


■実証コード

C:\C>Ms05-047.exe
[-] Usage: Ms05-047.exe <host>

C:\C>Ms05-047.exe 192.168.221.180
[+] Start connect host 192.168.221.180 ...
[+] Start bind RPC interface ...
[+] Start send RPC request ...
[-] TransactNamedPipe (Binding) failed !


■影響

攻撃は失敗しました。OSの再起動を確認する。

■Proventia検知


Event Number : 1
Date/Time : 2006-01-06 07:31:26 JST
Tag Name : MSRPC_PlugAndPlay_DeviceSlashBo
Alert Name : MSRPC_PlugAndPlay_DeviceSlashBo
Severity : High
Tag Brief Description :
Observance Type : Intrusion Detection
Combined Event Count : 1
Cleared Flag : No
Target DNS Name :
Target IP Address : 192.168.221.180
Target Object Name : 445
Target Object Type : Target Port
Target Service :
Source DNS Name :
Source IP Address : 192.168.221.11
SourcePort Name : 1082
Sensor DNS Name : iss-sp2
Sensor IP Address : 10.4.6.100
Sensor Name : network_sensor_1

Attribute Value Pairs for Event Number : 1
Attribute Name : :intruder-ip-addr
Attribute Value : 192.168.221.11
Attribute Name : :intruder-port
Attribute Value : 1082
Attribute Name : :Opnum
Attribute Value : 0xA
Attribute Name : :victim-ip-addr
Attribute Value : 192.168.221.180
Attribute Name : :victim-port
Attribute Value : 445
Attribute Name : algorithm-id
Attribute Value : 2118048
Attribute Name : IANAProtocolId
Attribute Value : 6
Attribute Name : LOGEVIDENCE
Attribute Value : Default
Attribute Name : Packet DestinationAddress
Attribute Value : 192.168.221.180
Attribute Name : Packet DestinationPort
Attribute Value : 445
Attribute Name : Packet DestinationPortName
Attribute Value : microsoft-ds
Attribute Name : Packet SourceAddress
Attribute Value : 192.168.221.11
Attribute Name : Packet SourcePort
Attribute Value : 1082


■snort検知

N/A

----------------------------
■あまてらす
----------------------------

おはようございます。あまてらすです。

Amebaブログのスクラップブックという機能の使い方がわかったような。

多分、ソーシャル・ネットワーキングサイト [mixi(ミクシィ)]のパクリみたいな感じなのかな?

登録したメンバー以外の人には、内容を公開しない機能があるみたいな・・・・

http://ameblo.jp/amaterasu/entry-10007730124.html の追加情報て

皆さんの端末から閲覧できなければ、私の認識であってる思うのですが・・・

だれか確認していただけると嬉しいです。

内容は、中国のサイトで公開されていたMS05-055の実証コードに関する解説になります。

結果教えてください。


----------------------------
■不正なアクセス(日本を送信元とした攻撃)
----------------------------


自分の管理するグローバルIPアドレスが以下のリストに含まれている場合は、ウィルスまたはボットワームに感染している恐れが高いです。至急ウィルススキャンを実行される事を推奨します。


61.125.227.51 i227051.ppp.asahi-net.or.jp
60.40.203.110 p2110-ipad10yamaguchi.yamaguchi.ocn.ne.jp
58.88.60.50 p1050-ipbf912marunouchi.tokyo.ocn.ne.jp
219.111.177.39 p6fb127.ymgcnt01.ap.so-net.ne.jp
218.45.67.153 218.45.67.153.eo.eaccess.ne.jp
218.45.54.248 fla03-248.wind.ne.jp
218.45.53.75 fla02-075.wind.ne.jp
218.45.53.183 fla02-183.wind.ne.jp
218.45.3.51 ppp31.aikis.or.jp
218.45.22.193 flets22-193.kamome.or.jp
218.45.20.203 218-45-20-203.flets.kamome.or.jp
218.45.179.242 k179242.ppp.asahi-net.or.jp
218.45.174.203 k174203.ppp.asahi-net.or.jp
218.45.174.197 k174197.ppp.asahi-net.or.jp
218.45.173.65 k173065.ppp.asahi-net.or.jp
218.45.172.81 k172081.ppp.asahi-net.or.jp
218.45.170.123 k170123.ppp.asahi-net.or.jp
218.45.169.90 k169090.ppp.asahi-net.or.jp
218.45.168.253 k168253.ppp.asahi-net.or.jp
218.45.168.225 k168225.ppp.asahi-net.or.jp
218.45.166.1 k166001.ppp.asahi-net.or.jp
218.45.165.198 k165198.ppp.asahi-net.or.jp
218.45.164.52 k164052.ppp.asahi-net.or.jp
218.45.164.247 k164247.ppp.asahi-net.or.jp
218.45.139.41 u21845139041.hctv.ne.jp
218.45.139.33 u21845139033.hctv.ne.jp
218.45.111.6 flets-a-west-24-6.dsn.jp
218.45.11.45 f1315.nnc.or.jp
218.45.109.25 flets-a-west-14-25.dsn.jp
218.45.107.7 flets-a-west-12-7.dsn.jp
218.44.97.239 i218-44-97-239.s02.a038.ap.plala.or.jp
218.44.68.50 i218-44-68-50.s02.a035.ap.plala.or.jp
218.44.51.50 f51.50.fgo.jp
218.44.27.229 i218-44-27-229.s02.a021.ap.plala.or.jp
218.43.40.189 p2189-ipbf410marunouchi.tokyo.ocn.ne.jp
218.43.35.135 p1135-ipbf409marunouchi.tokyo.ocn.ne.jp
218.43.3.235 p4235-ipad02niigatani.niigata.ocn.ne.jp
218.43.235.83 p6083-ipad01sinnagasak.nagasaki.ocn.ne.jp
218.43.206.188 p1188-ipad11sasajima.aichi.ocn.ne.jp
218.43.2.121 p3121-ipad02niigatani.niigata.ocn.ne.jp
218.43.190.165 p6165-ipad01motosinmat.mie.ocn.ne.jp
218.43.166.94 p5094-ipad02fukuokachu.fukuoka.ocn.ne.jp
218.43.157.46 p3046-ipad02yamaguchi.yamaguchi.ocn.ne.jp
218.42.201.104 218-42-201-104.eonet.ne.jp
218.41.40.86 p292856.szoknt01.ap.so-net.ne.jp
218.41.39.221 p2927dd.szoknt01.ap.so-net.ne.jp
218.41.38.24 p292618.ibrknt01.ap.so-net.ne.jp
218.41.29.28 p291d1c.hyognt01.ap.so-net.ne.jp
218.41.23.219 p2917db.fkoknt01.ap.so-net.ne.jp
218.41.19.19 p291313.sitmnt01.ap.so-net.ne.jp
218.41.15.131 p290f83.sitmnt01.ap.so-net.ne.jp
218.41.143.200 p298fc8.tkyoac00.ap.so-net.ne.jp
218.41.115.35 p297323.ibrknt01.ap.so-net.ne.jp
218.40.16.62 da2810-062.tiki.ne.jp
218.33.138.190 218.33.138.190.eo.eaccess.ne.jp
218.231.115.20 218.231.115.20.eo.eaccess.ne.jp
218.229.36.88 ntmiex012088.miex.nt.adsl.ppp.infoweb.ne.jp
218.218.139.247 AKAfa-01p4-247.ppp11.odn.ad.jp
218.110.88.149 p6e5895.ymgcnt01.ap.so-net.ne.jp
218.110.85.157 p6e559d.sigant01.ap.so-net.ne.jp


----------------------------
■snortサマリーレポート
----------------------------

- traffic_summary.py 0.17(2005-07-20)

Report Settings:
- Honeynet: 192.168.37.0/24
- Starting Date: 20060105 (inclusive)
- Ending Date: 20060106 (exclusive)
- Number of days: 1
- Output file: /tmp/.sum.kyGn3162


Total pcap records processed: 6,887
Total snort records processed: 1,904

========================================
Summary
=======

Remote IP Count: 284
Ports Scanned: 36

Connection Packets Packets Bytes Bytes
Type Count In Out In Out
-------- --------- --------- --------- --------- ---------
Inbound 2699 19494 16602 1645732 869049
Outbound 46 394 394 27734 27734

Total Snort SIDs: 12
Total Snort Alerts: 1904

========================================
Top 10 Snort Alerts
===================

Count SID Alert Description
----- ------ ---------------------------------
925 2 (spp_stream4) possible EVASIVE RST detection
697 2403 NETBIOS SMB Session Setup AndX request unicode username overflow attempt
160 2404 NETBIOS SMB-DS Session Setup AndX request unicode username overflow attempt
69 2923 NETBIOS SMB repeated logon failure
19 2924 NETBIOS SMB-DS repeated logon failure
18 402 ICMP Destination Unreachable Port Unreachable
5 2251 NETBIOS DCERPC Remote Activation bind attempt
5 3276 NETBIOS DCERPC IActivation little endian bind attempt
2 1390 SHELLCODE x86 inc ebx NOOP
2 15 (http_inspect) OVERSIZE REQUEST-URI DIRECTORY
1 2466 NETBIOS SMB-DS IPC$ unicode share access

========================================
All Snort Alerts
================

Count SID Alert Description
----- ------ ---------------------------------
925 2 (spp_stream4) possible EVASIVE RST detection
2 15 (http_inspect) OVERSIZE REQUEST-URI DIRECTORY
18 402 ICMP Destination Unreachable Port Unreachable
1 538 NETBIOS SMB IPC$ unicode share access
2 1390 SHELLCODE x86 inc ebx NOOP
5 2251 NETBIOS DCERPC Remote Activation bind attempt
697 2403 NETBIOS SMB Session Setup AndX request unicode username overflow attempt
160 2404 NETBIOS SMB-DS Session Setup AndX request unicode username overflow attempt
1 2466 NETBIOS SMB-DS IPC$ unicode share access
69 2923 NETBIOS SMB repeated logon failure
19 2924 NETBIOS SMB-DS repeated logon failure
5 3276 NETBIOS DCERPC IActivation little endian bind attempt

========================================
Top 10 Scanned Ports:
=====================

Port Packets Bytes Conns
--------- --------- --------- ---------
tcp/139 16485 1062837 1463
tcp/445 11464 1275292 744
tcp/135 1945 56460 240
tcp/5000 316 0 51
tcp/80 332 56560 39
udp/137 56 9828 29
tcp/1433 5244 32961 26
udp/1026 21 8089 21
udp/1027 22 8260 19
tcp/4899 56 0 15

■脆弱性の説明MSMS05-055

http://www.microsoft.com/japan/technet/security/Bulletin/MS05-055.mspx

http://xforce.iss.net/xforce/bulletins/microsoft/MS05-055

■実証コード

C:\>ms05-055 helper.exe

MS05-055 Windows Kernel APC Data-Free Local Privilege Escalation Vulnerability
Exploit

Create by SoBeIt.

Child ESP:be9a9c0c
PoolIndex:9b PoolType:9a
Perfect ESP:be9a9c0c
The sleep has awaken.
Target thread handle:3c0, Target process handle:3d8, Process id:70
helper.exe 960 112
Now waitting for triggering the bug.
Got thread handle:3c0, Got process id:70
Process handle:3d4
Now terminating process.
Parent process id:c4
In child thread. Now terminating to trigger the bug.
Exploit finished.

C:\>whoami
NT AUTHORITY\SYSTEM

C:\>


■Proventia検知

Local Overflowの為、検知なし


■snort検知

Local Overflowの為、検知なし


■パケット

Local Overflowの為、パケット検知なし


----------------------------
■あまてらす
----------------------------
今日からお仕事です。2日出社して3連休。早くお休みこないかな~~~あ。

昨日紹介しました。旅行中ある空港の45番ゲートの表示は、

「Tel Aviv」でした。日本語だとどう書くのでしょう?

0104_02

----------------------------
■不正なアクセス(日本を送信元とした攻撃)
----------------------------

自分の管理するグローバルIPアドレスが以下のリストに含まれている場合は、ウィルスまたはボットワームに感染している恐れが高いです。至急ウィルススキャンを実行される事を推奨します。


61.199.121.204 p5204-ipad01gifu.gifu.ocn.ne.jp
61.125.78.249 zaq3d7d4ef9.zaq.ne.jp
61.125.73.95 zaq3d7d495f.zaq.ne.jp
61.125.68.233 zaq3d7d44e9.zaq.ne.jp
61.125.66.119 zaq3d7d4277.zaq.ne.jp
61.125.57.153 usr021.bb007-01.uda.im.wakwak.ne.jp
61.125.249.56 i249056.ppp.asahi-net.or.jp
61.125.247.243 i247243.ppp.asahi-net.or.jp
61.125.228.83 i228083.ppp.asahi-net.or.jp
61.125.212.177 i212177.ppp.asahi-net.or.jp
61.125.193.73 i193073.ppp.asahi-net.or.jp
61.125.106.216 zaq3d7d6ad8.zaq.ne.jp
61.125.104.91 zaq3d7d685b.zaq.ne.jp
61.125.101.18 zaq3d7d6512.zaq.ne.jp
61.124.219.143 nthygo017143.hygo.nt.adsl.ppp.infoweb.ne.jp
61.124.212.103 ntaich018103.aich.nt.adsl.ppp.infoweb.ne.jp
61.123.223.101 client.mcbnet.ne.jp
61.117.82.67 M082067.ppp.dion.ne.jp
60.42.170.49 i60-42-170-49.s05.a043.ap.plala.or.jp
58.93.20.103 i58-93-20-103.s05.a013.ap.plala.or.jp
221.185.64.248 p1248-ipad42sasajima.aichi.ocn.ne.jp
220.221.121.173 i220-221-121-173.s02.a040.ap.plala.or.jp
219.98.204.186 p62ccba.tkyoac00.ap.so-net.ne.jp
219.107.178.183 FLA1Aah183.fko.mesh.ad.jp
218.45.6.55 f309.nnc.or.jp
218.45.53.25 fla02-025.wind.ne.jp
218.45.53.226 fla02-226.wind.ne.jp
218.45.51.88 fla01-088.wind.ne.jp
218.45.5.59 f059.nnc.or.jp
218.45.3.62 ppp42.aikis.or.jp
218.45.183.19 k183019.ppp.asahi-net.or.jp
218.45.175.165 k175165.ppp.asahi-net.or.jp
218.45.173.103 k173103.ppp.asahi-net.or.jp
218.45.172.13 k172013.ppp.asahi-net.or.jp
218.45.168.222 k168222.ppp.asahi-net.or.jp
218.45.165.237 k165237.ppp.asahi-net.or.jp
218.45.163.108 k163108.ppp.asahi-net.or.jp
218.45.139.41 u21845139041.hctv.ne.jp
218.45.139.33 u21845139033.hctv.ne.jp
218.45.110.43 flets-a-west-15-43.dsn.jp
218.45.11.74 f1344.nnc.or.jp
218.45.108.69 flets-a-west-13-69.dsn.jp
218.45.107.169 flets-a-west-12-169.dsn.jp
218.45.106.81 flets-a-west-11-81.dsn.jp
218.45.105.170 flets-a-west-10-170.dsn.jp
218.45.104.201 flets-a-west-9-201.dsn.jp
218.45.100.165 bflets-fm-west-3-165.dsn.jp
218.44.84.128 i218-44-84-128.s02.a018.ap.plala.or.jp
218.44.52.209 f52.209.fgo.jp
218.44.43.155  
218.44.124.27 i218-44-124-27.s02.a027.ap.plala.or.jp
218.44.117.202 i218-44-117-202.s02.a015.ap.plala.or.jp
218.44.107.149 i218-44-107-149.s02.a045.ap.plala.or.jp
218.43.222.11 p5011-ipad01matuyama.ehime.ocn.ne.jp
218.229.234.49 hcou120049.catv.ppp.infoweb.ne.jp
218.224.190.130 i218-224-190-130.s04.a022.ap.plala.or.jp
218.220.84.72 zaqdadc5448.zaq.ne.jp
218.218.172.120 FKCfb-01p1-120.ppp11.odn.ad.jp
211.9.145.1 bu1.opt2.point.ne.jp
202.216.50.17 flets-a-west-3-17.dsn.jp

----------------------------
■snortサマリー
----------------------------

traffic_summary.py 0.17(2005-07-20)

Report Settings:
- Honeynet: 192.168.37.0/24
- Starting Date: 20060104 (inclusive)
- Ending Date: 20060105 (exclusive)
- Number of days: 1
- Output file: /tmp/.sum.edW23496


Total pcap records processed: 5,450
Total snort records processed: 3,678

========================================
Summary
=======

Remote IP Count: 328
Ports Scanned: 54

Connection Packets Packets Bytes Bytes
Type Count In Out In Out
-------- --------- --------- --------- --------- ---------
Inbound 2332 15624 13010 1912203 941509
Outbound 558 16539 16539 19485597 19485597

Total Snort SIDs: 25
Total Snort Alerts: 3678

========================================
Top 10 Snort Alerts
===================

Count SID Alert Description
----- ------ ---------------------------------
1742 2 (spp_stream4) possible EVASIVE RST detection
1504 2404 NETBIOS SMB-DS Session Setup AndX request unicode username overflow attempt
145 2924 NETBIOS SMB-DS repeated logon failure
96 1390 SHELLCODE x86 inc ebx NOOP
24 1709 WEB-CGI ad.cgi access
24 2251 NETBIOS DCERPC Remote Activation bind attempt
24 3276 NETBIOS DCERPC IActivation little endian bind attempt
21 402 ICMP Destination Unreachable Port Unreachable
14 15 (http_inspect) OVERSIZE REQUEST-URI DIRECTORY
13 1070 WEB-MISC WebDAV search access
12 2466 NETBIOS SMB-DS IPC$ unicode share access

========================================
Top 10 Scanned Ports:
=====================

Port Packets Bytes Conns
--------- --------- --------- ---------
tcp/139 6927 373016 1024
tcp/445 18506 1888391 844
tcp/135 1242 32626 166
tcp/80 1077 510145 69
udp/137 68 11610 34
tcp/4444 128 0 33
udp/1026 32 12108 26
udp/1027 24 8247 19
tcp/1433 290 2821 18
tcp/3389 38 0 16

========================================

■脆弱性の説明MS05-037

http://www.microsoft.com/japan/technet/security/Bulletin/MS05-037.mspx

http://xforce.iss.net/xforce/bulletins/microsoft/MS05-037


■攻撃元(受動的攻撃)

192.168.221.110 RedHat


■攻撃対象

192.168.221.180 Win2K English


■実証コード

C:\C>MS05-037.pl > test.html

■Proventia

DHTML_Object_Overflow
http://xforce.iss.net/xforce/xfdb/19831

HTML_IE_Javaprxy_Heap_Corruption

http://www.iss.net/security_center/static/21193.php


Event Number : 3
Date/Time : 2006-01-04 18:23:43 JST
Tag Name : DHTML_Object_Overflow
Alert Name : DHTML_Object_Overflow
Severity : High
Tag Brief Description :
Observance Type : Intrusion Detection
Combined Event Count : 1
Cleared Flag : No
Target DNS Name :
Target IP Address : 192.168.221.106
Target Object Name : 8287
Target Object Type : Target Port
Target Service :
Source DNS Name :
Source IP Address : 192.168.221.110
SourcePort Name : 80
Sensor DNS Name : iss-sp2
Sensor IP Address : 10.4.6.100
Sensor Name : network_sensor_1

Attribute Value Pairs for Event Number : 3
Attribute Name : :accessed
Attribute Value : yes
Attribute Name : :code
Attribute Value : 200
Attribute Name : :intruder-ip-addr
Attribute Value : 192.168.221.110
Attribute Name : :intruder-port
Attribute Value : 80
Attribute Name : :protocol
Attribute Value : http
Attribute Name : :server
Attribute Value : 192.168.221.110
Attribute Name : :URL
Attribute Value : /test.html
Attribute Name : :victim-ip-addr
Attribute Value : 192.168.221.106
Attribute Name : :victim-port
Attribute Value : 8287
Attribute Name : algorithm-id
Attribute Value : 2113203
Attribute Name : IANAProtocolId
Attribute Value : 6
Attribute Name : LOGEVIDENCE
Attribute Value : Default
Attribute Name : Packet DestinationAddress
Attribute Value : 192.168.221.110
Attribute Name : Packet DestinationPort
Attribute Value : 80
Attribute Name : Packet DestinationPortName
Attribute Value : http
Attribute Name : Packet SourceAddress
Attribute Value : 192.168.221.106
Attribute Name : Packet SourcePort
Attribute Value : 8287


Event Number : 4
Date/Time : 2006-01-04 18:43:11 JST
Tag Name : HTML_IE_Javaprxy_Heap_Corruption
Alert Name : HTML_IE_Javaprxy_Heap_Corruption
Severity : High
Tag Brief Description :
Observance Type : Intrusion Detection
Combined Event Count : 1
Cleared Flag : No
Target DNS Name :
Target IP Address : 192.168.221.106
Target Object Name : 8428
Target Object Type : Target Port
Target Service :
Source DNS Name :
Source IP Address : 192.168.221.110
SourcePort Name : 80
Sensor DNS Name : iss-sp2
Sensor IP Address : 10.4.6.100
Sensor Name : network_sensor_1

Attribute Value Pairs for Event Number : 4
Attribute Name : :accessed
Attribute Value : yes
Attribute Name : :code
Attribute Value : 200
Attribute Name : :intruder-ip-addr
Attribute Value : 192.168.221.110
Attribute Name : :intruder-port
Attribute Value : 80
Attribute Name : :protocol
Attribute Value : http
Attribute Name : :server
Attribute Value : 192.168.221.110
Attribute Name : :URL
Attribute Value : /ms05-037.html
Attribute Name : :victim-ip-addr
Attribute Value : 192.168.221.106
Attribute Name : :victim-port
Attribute Value : 8428
Attribute Name : algorithm-id
Attribute Value : 2106195
Attribute Name : IANAProtocolId
Attribute Value : 6
Attribute Name : LOGEVIDENCE
Attribute Value : Default
Attribute Name : Packet DestinationAddress
Attribute Value : 192.168.221.110
Attribute Name : Packet DestinationPort
Attribute Value : 80
Attribute Name : Packet DestinationPortName
Attribute Value : http
Attribute Name : Packet SourceAddress
Attribute Value : 192.168.221.106
Attribute Name : Packet SourcePort
Attribute Value : 8428
Attribute Name : RSKILL
Attribute Value : Default


■snort検知

N/A